A new class of AI for
cloud security
General AI understands text. OFFENSAI understands cloud attacks.
Its model reasons over a Universal Offensive Ontology, a shared attack language linking identities, permissions, and services into real cross-cloud chains, each validated in live environments

Why can't frontier models and LLM wrappers deliver effective cloud security validation?
Context windows break on cloud-scale graphs
Frontier models reason within a session; real cloud attack paths span millions of relationships and require a persistent graph.
No persistent attack memory
Each prompt starts from zero. Without persistent knowledge, frontier models can't build or evolve multi-step attack chains.
No native understanding of cloud attack logic
General AI understands language, not attack primitives; without a unified ontology, it can't link IAM abuse and APIs into cross-cloud chains.
Your attack surface leaves the perimeter
Using frontier APIs requires sending cloud context externally, exposing IAM topology and trust relationships.
No deterministic proof of exploitability
Frontier models generate answers, not validated outcomes; they can't prove attack paths, leaving assumptions instead of evidence.
A specialized AI foundation for cloud attacks
Connect discovery, proof, execution, and learning into a loop that improves with every validated attack path.
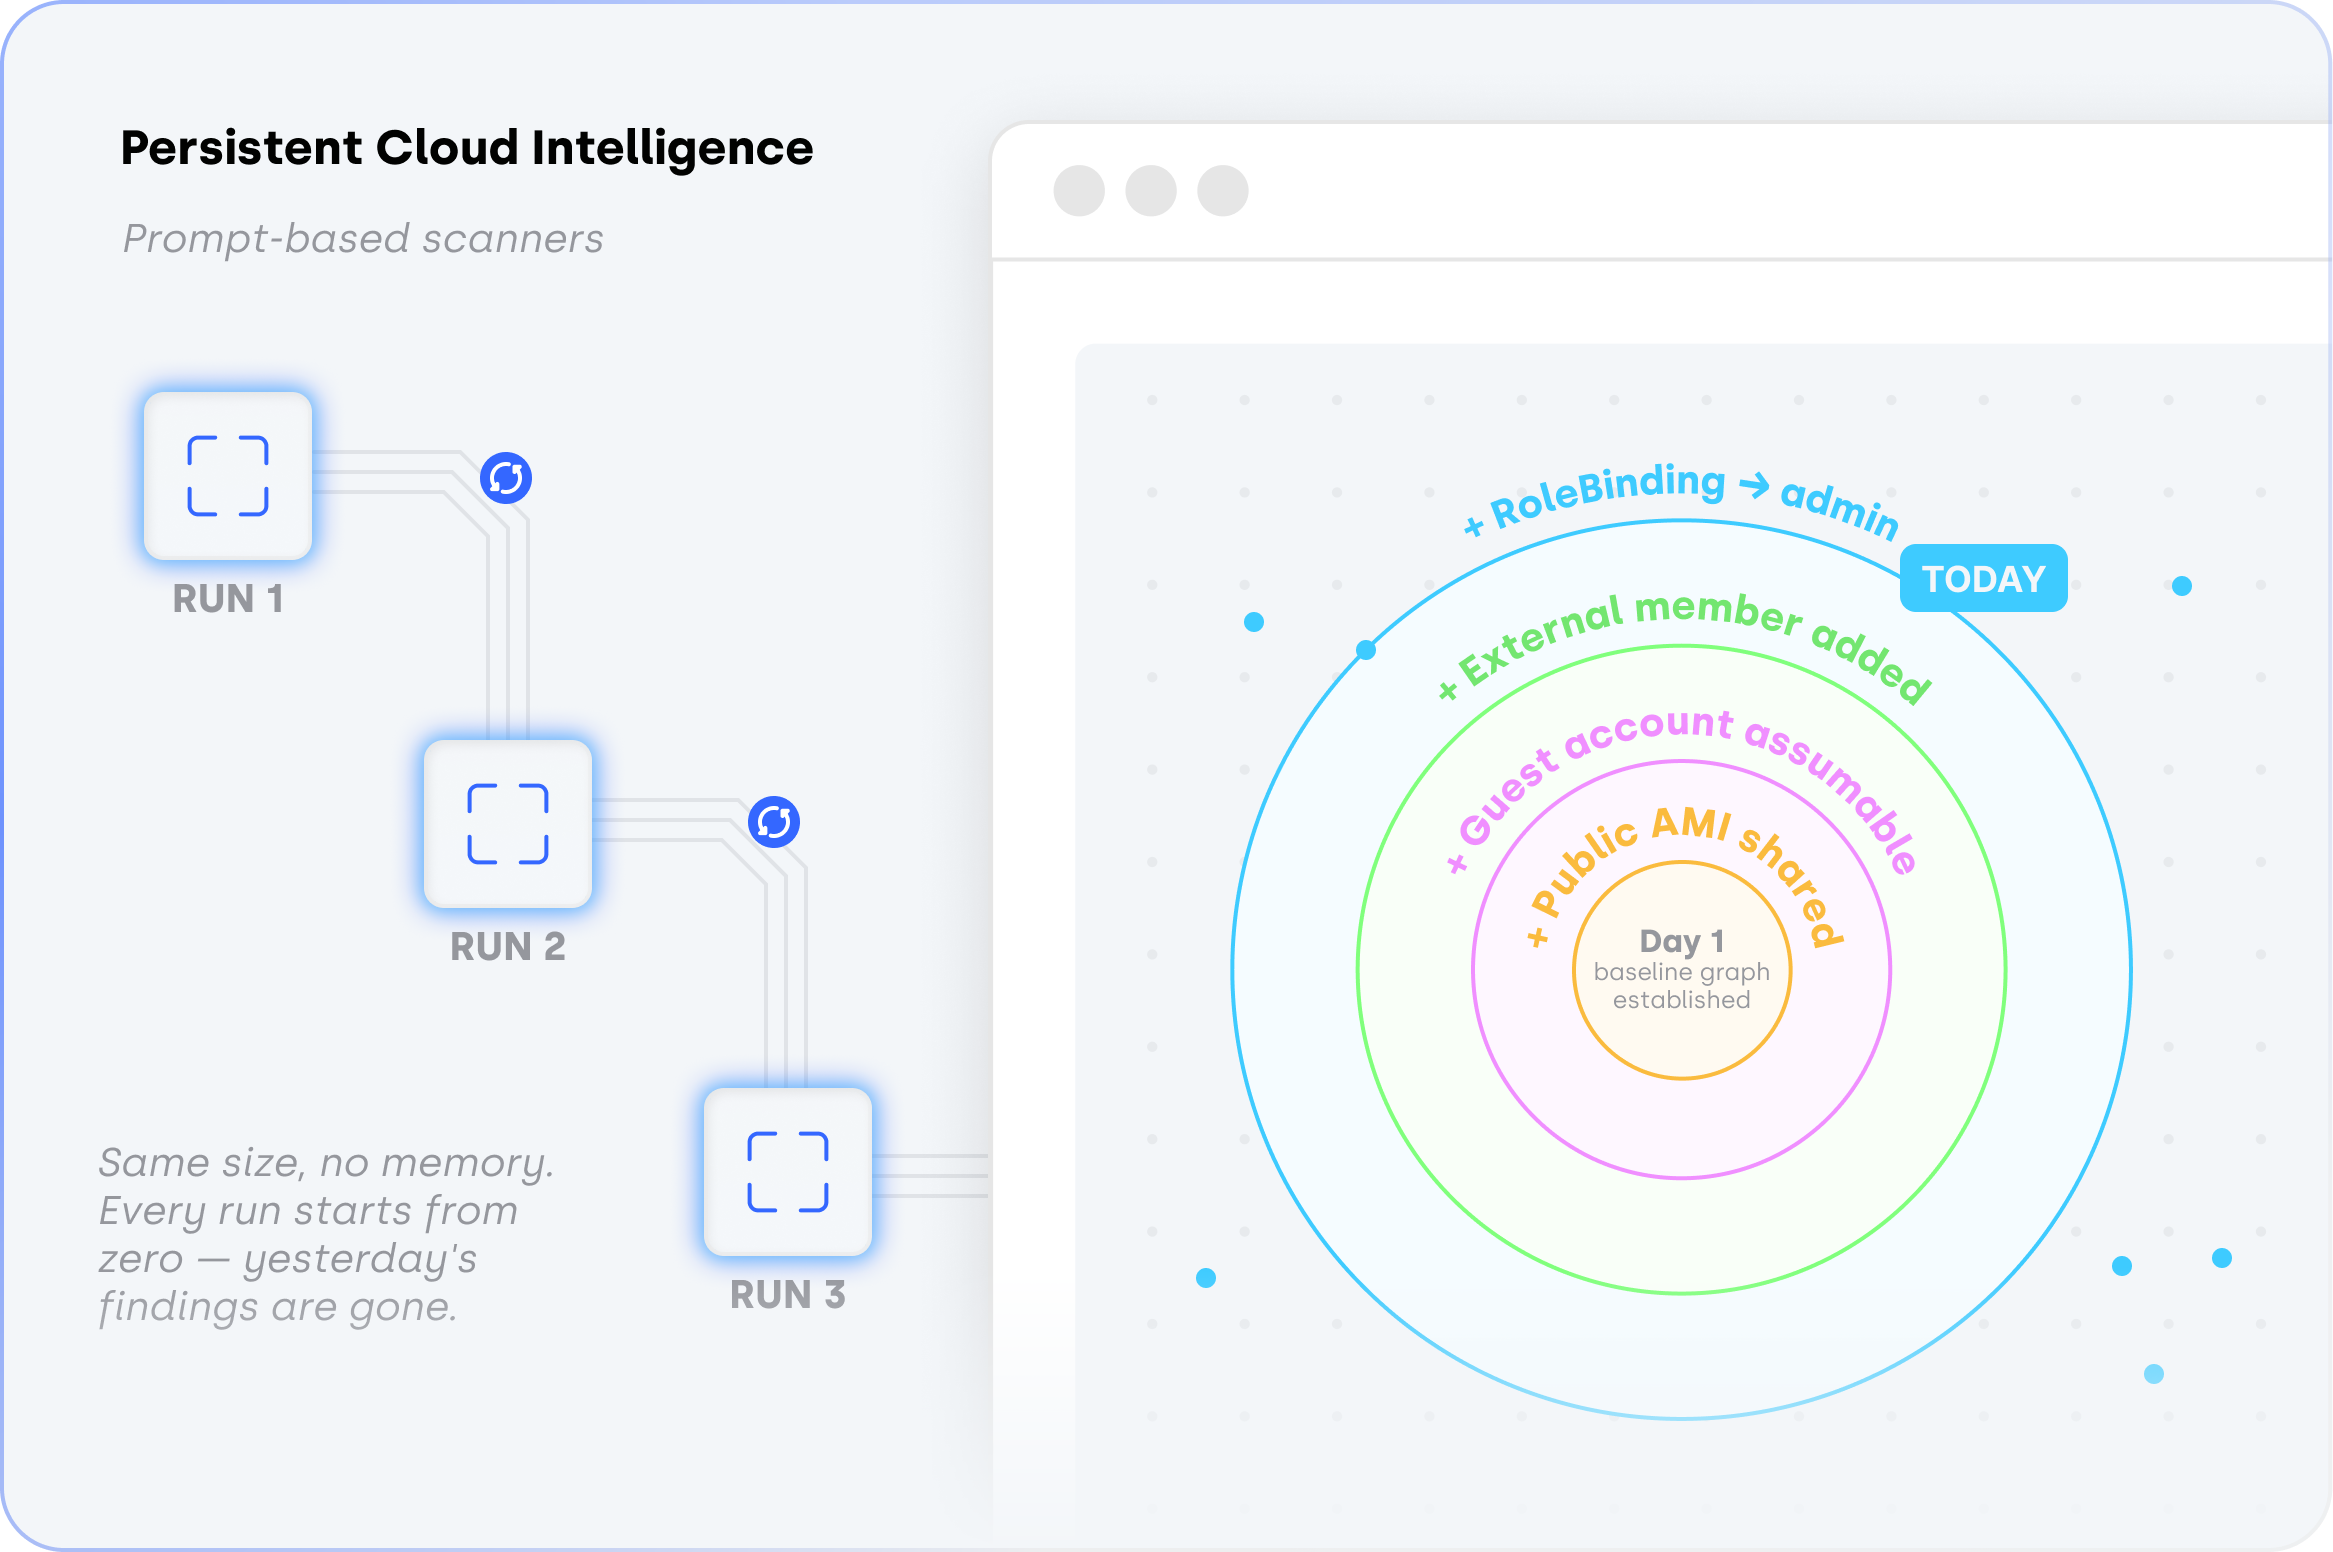
Persistent cloud intelligence
OFFENSAI finds exploitable cloud changes across AWS, Azure, GCP, and Kubernetes, feeding a persistent graph instead of resetting with each prompt.
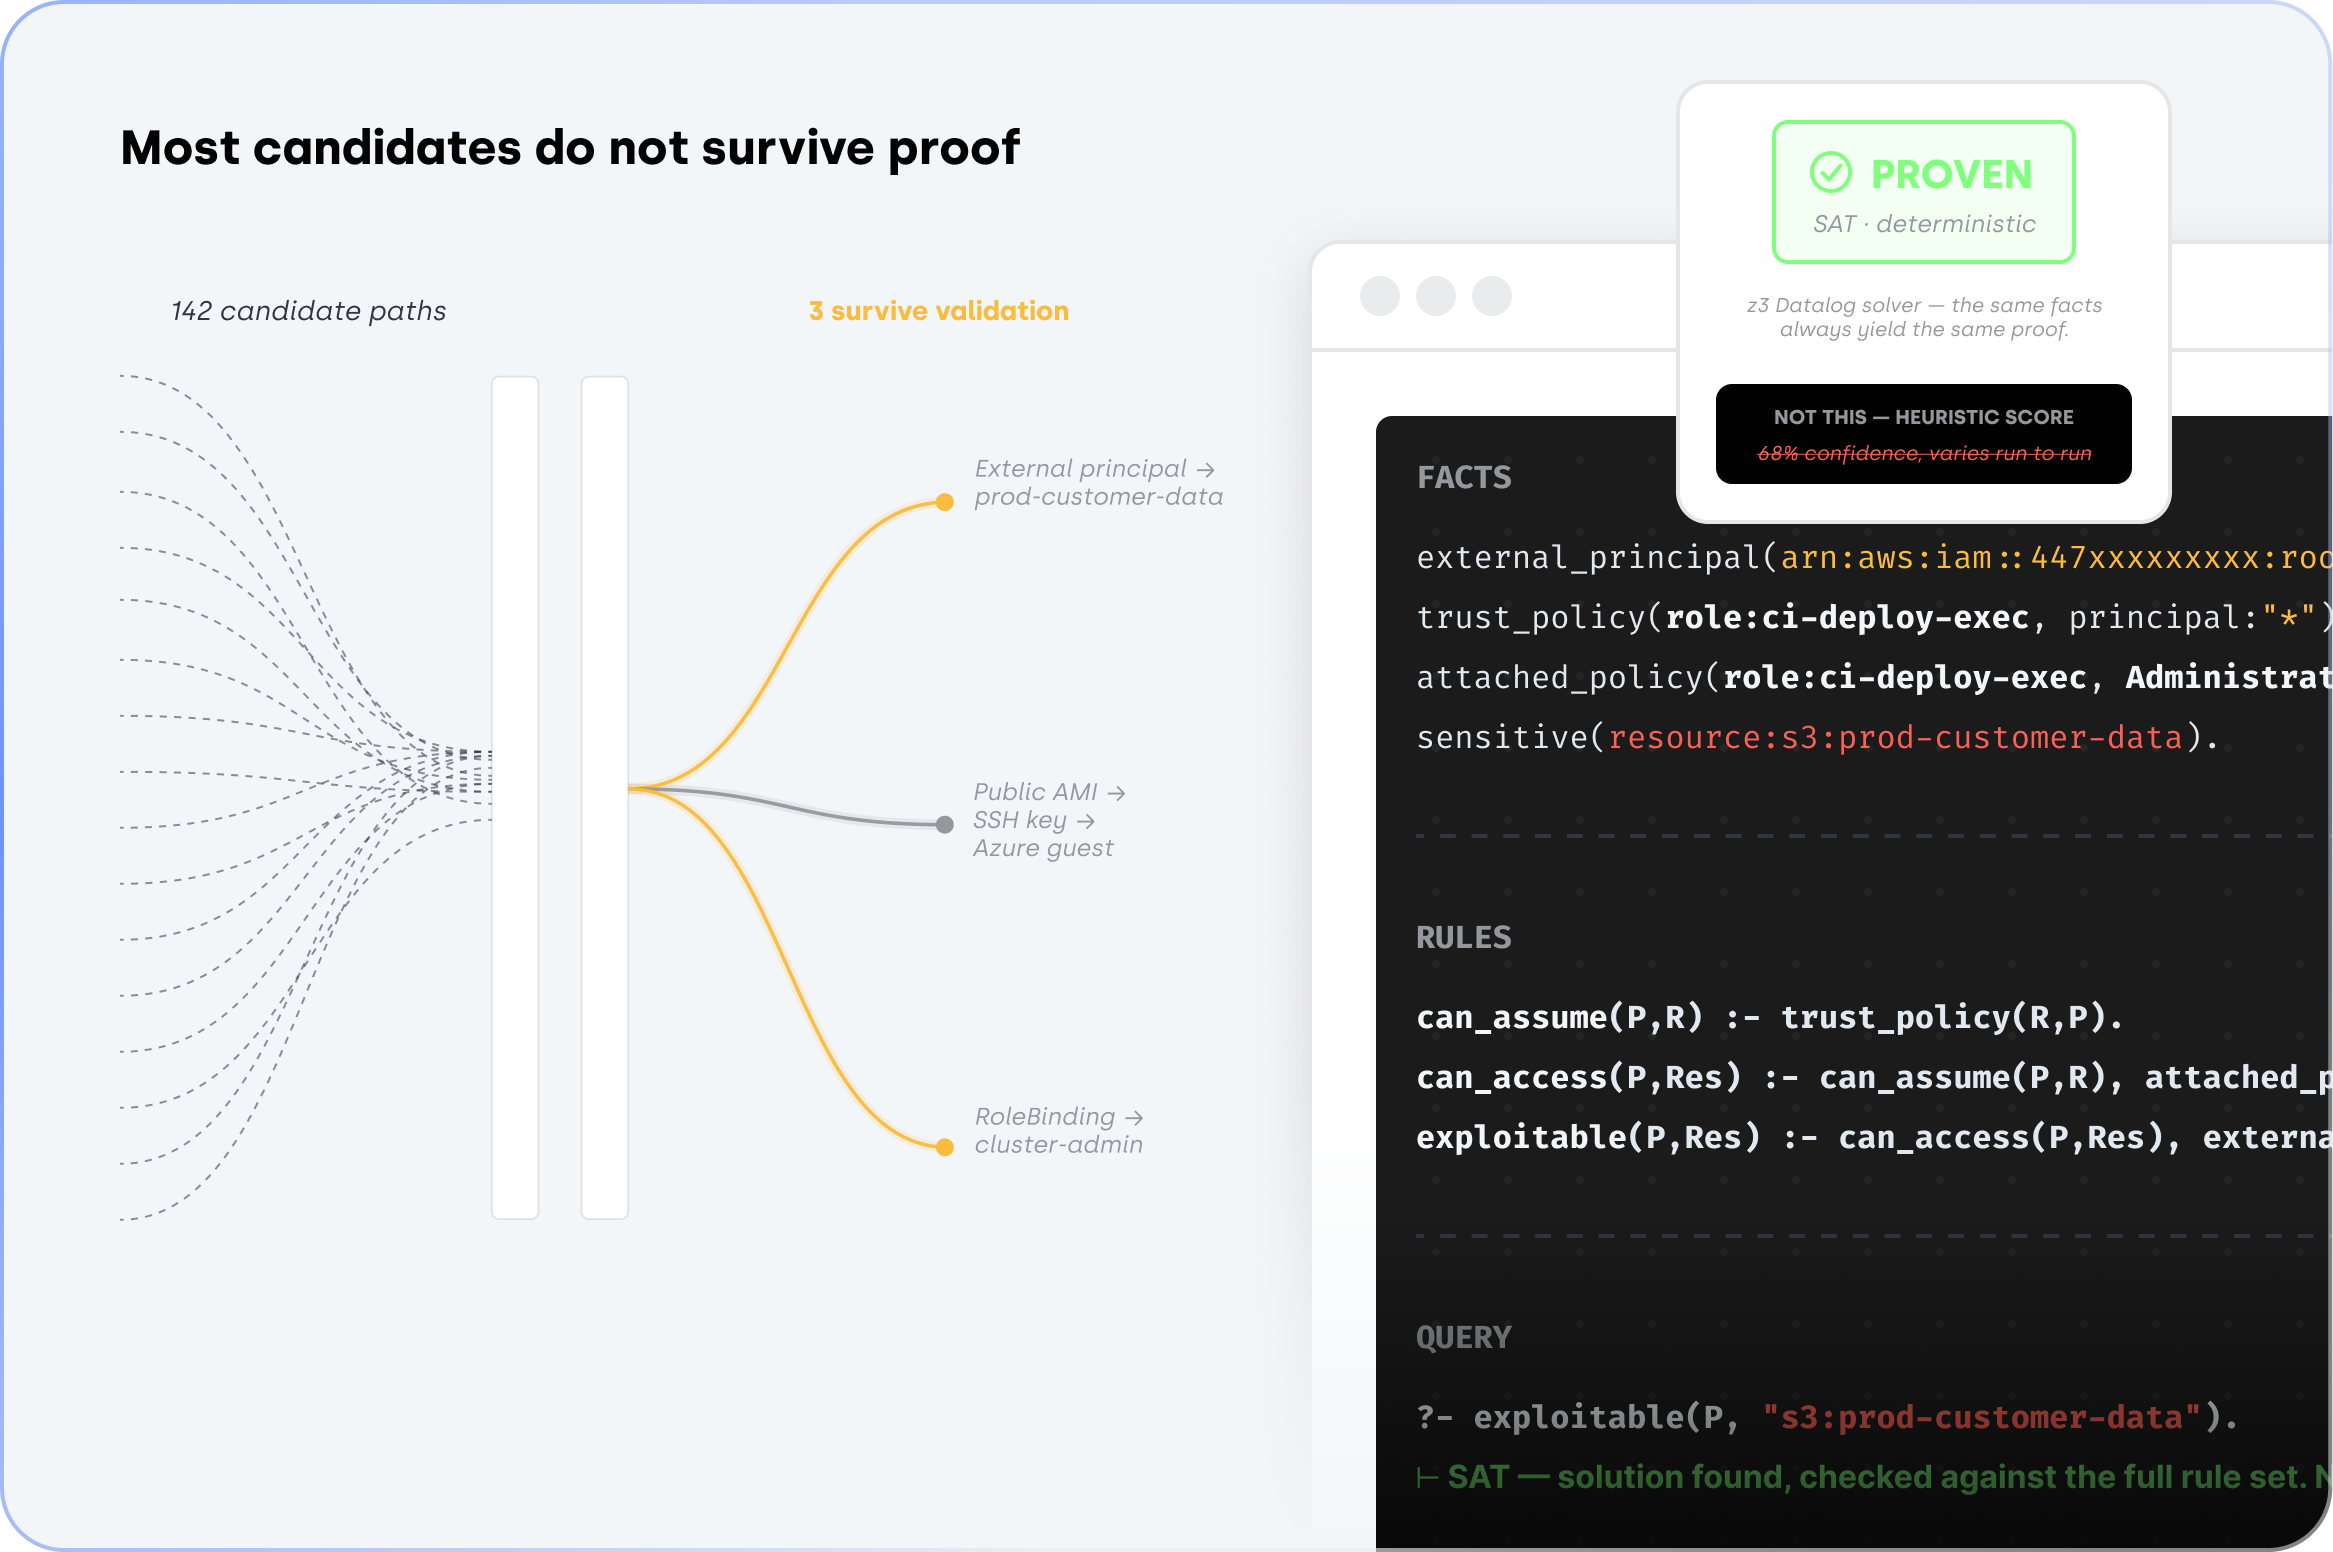
Formal proof engine
Mathematically proves which attack paths exist in your environment using z3 Datalog, delivering deterministic validation instead of probabilistic answers.
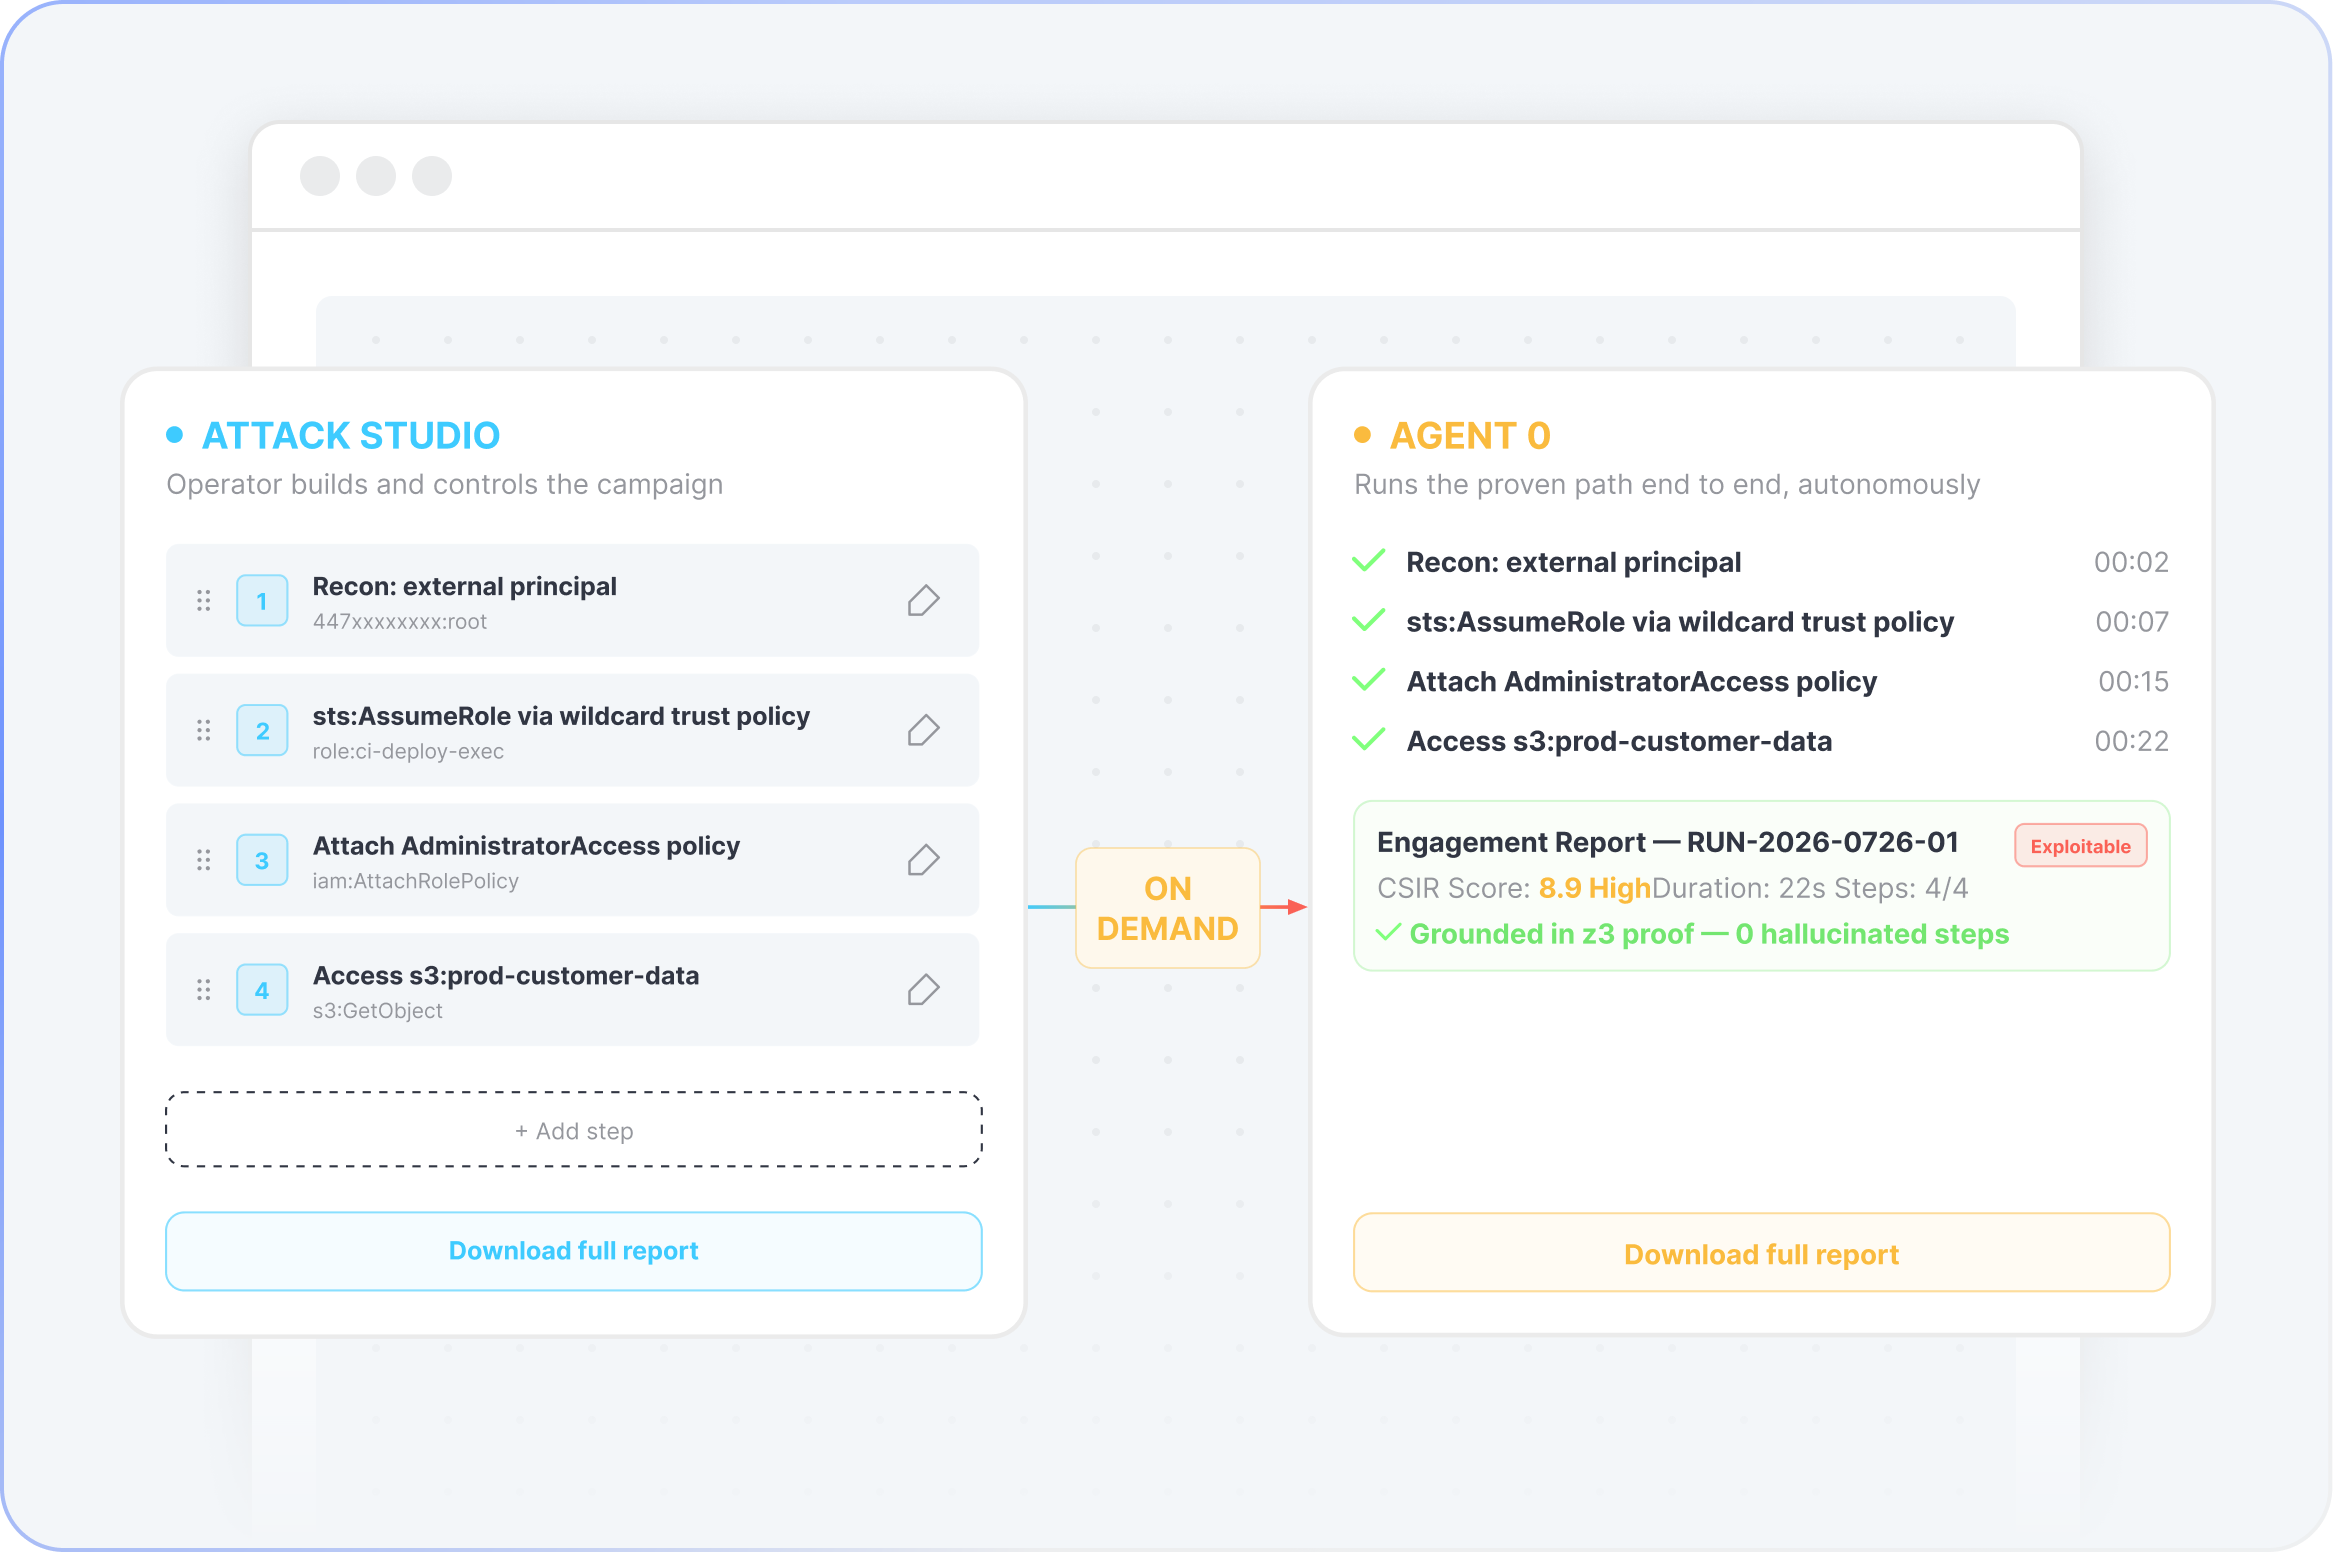
Execution layer: Operator-driven or autonomous
ATTACKSTUDIO™ lets operators build and control campaigns, while Agent O runs proven paths end to end, on demand with full reports and no hallucinations.
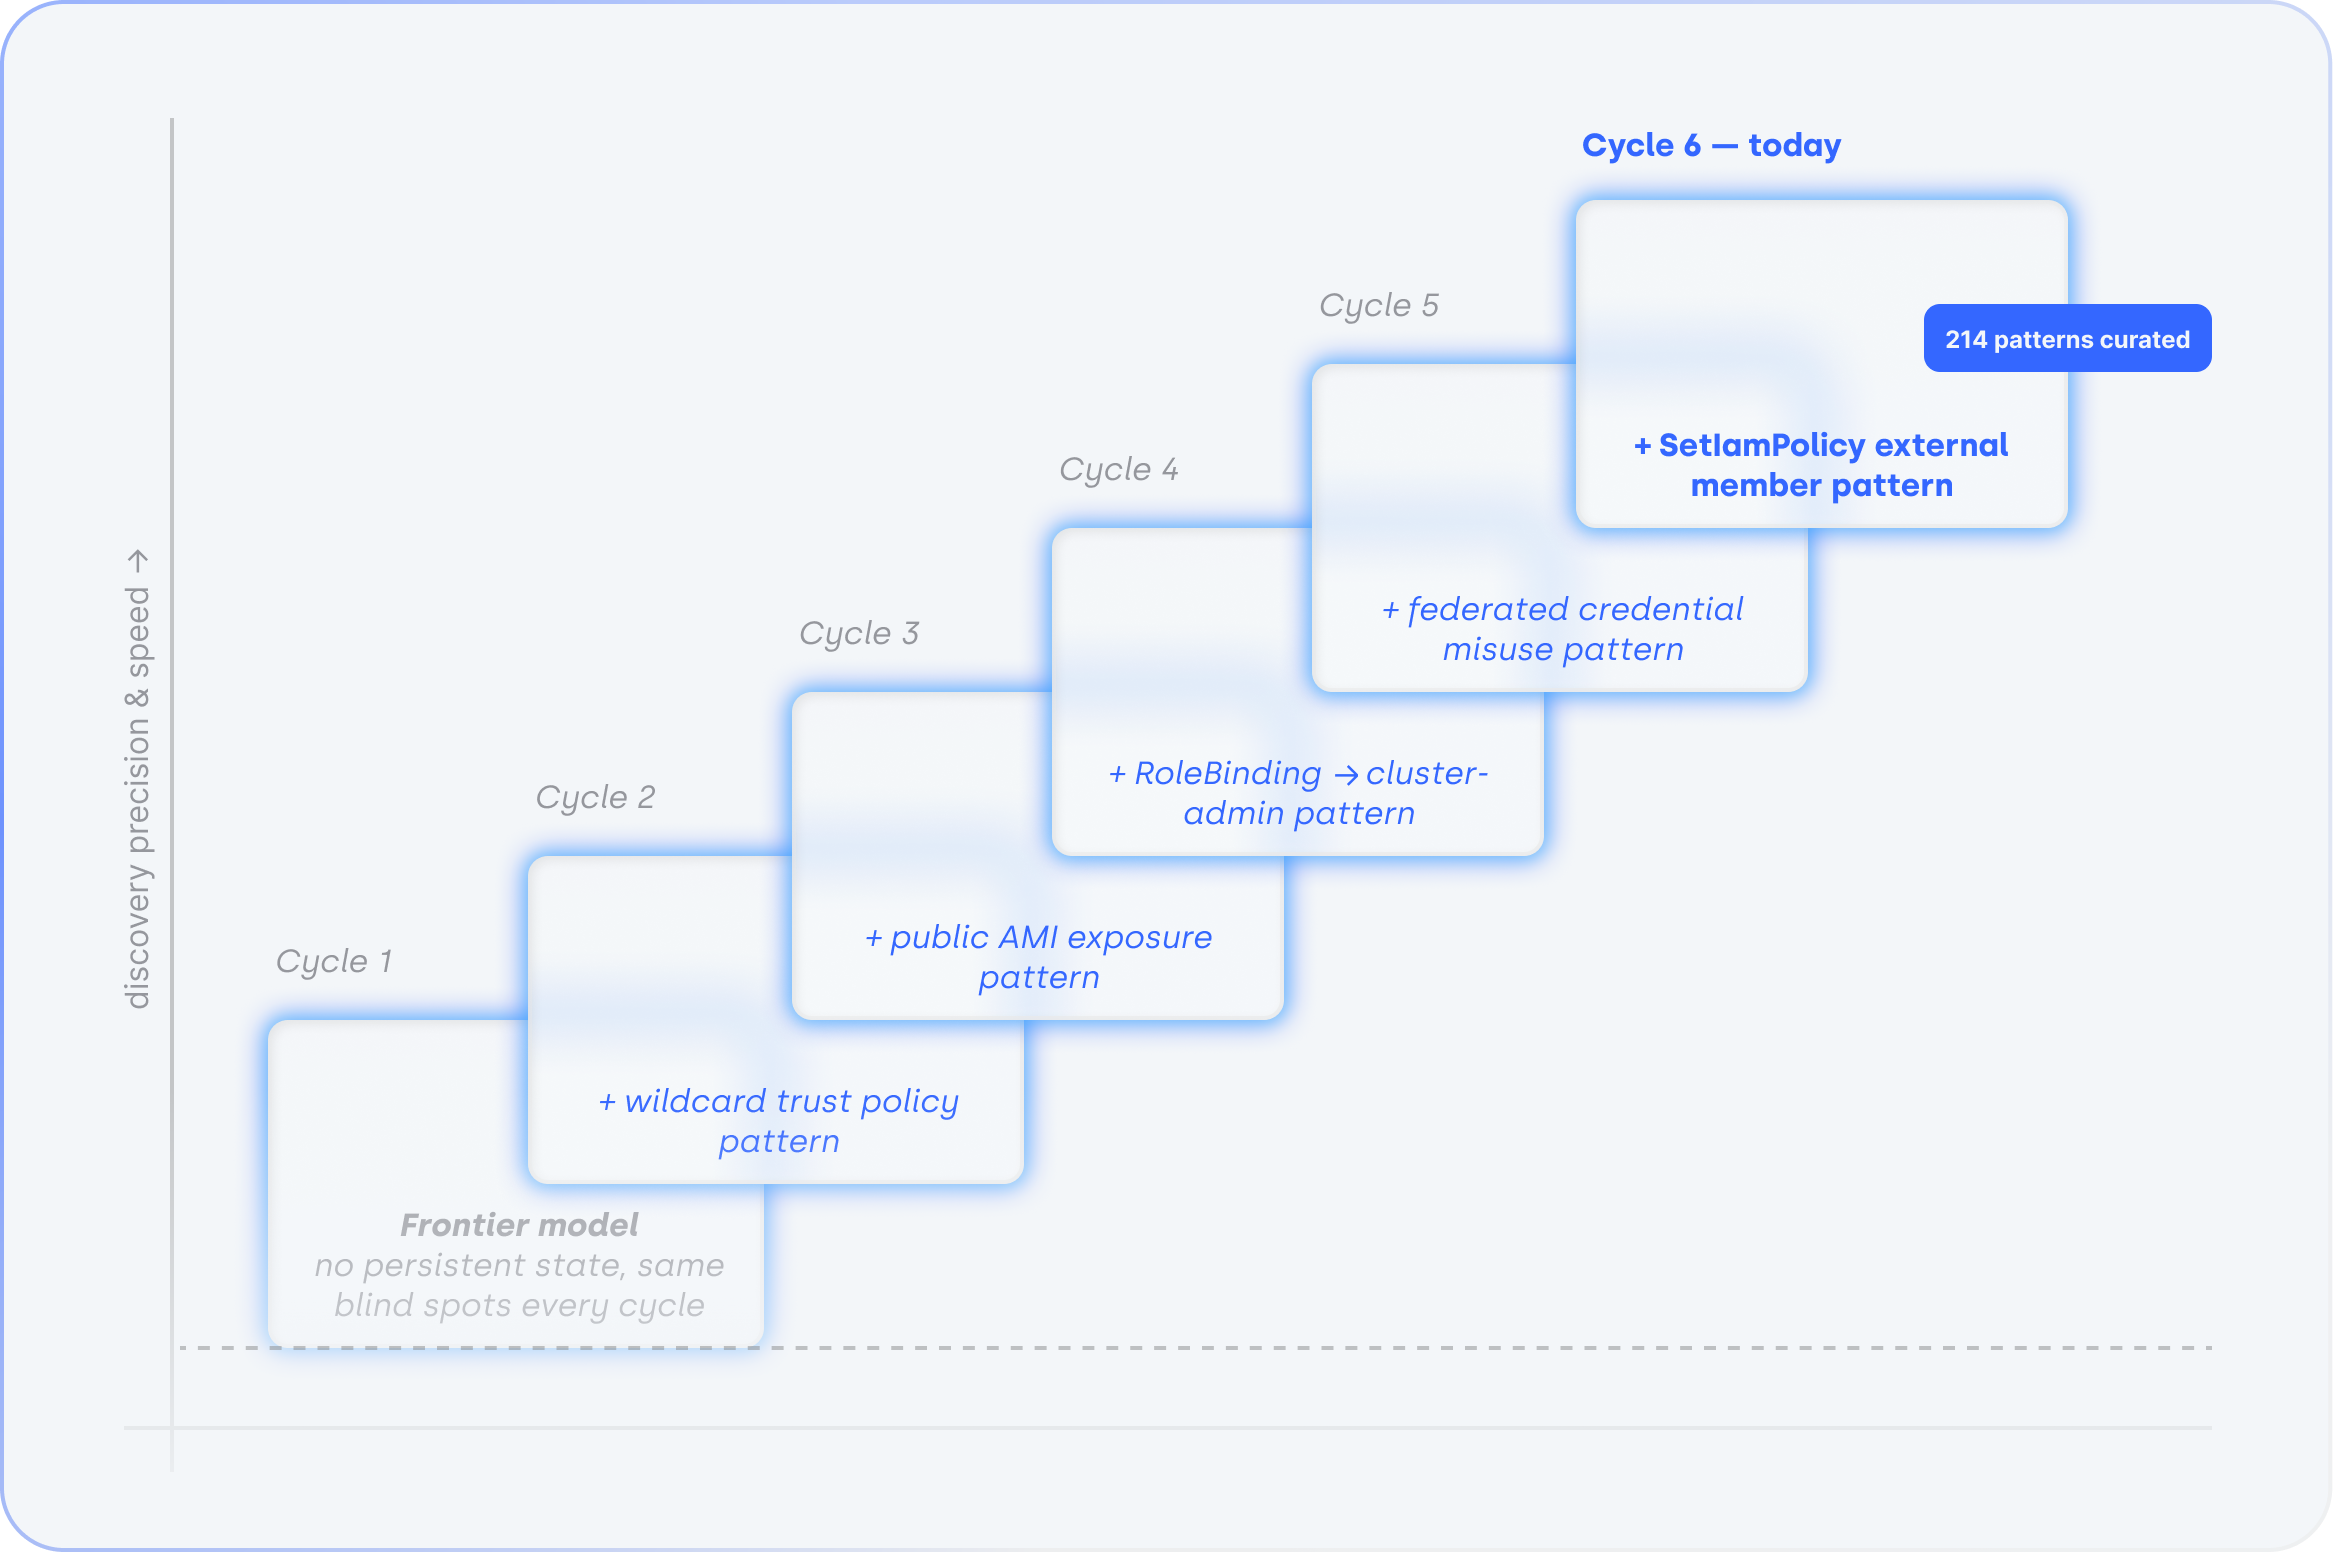
Compounding attack graph collection
Curates verified patterns into a compounding knowledge graph that sharpens every future discovery cycle, unlike frontier models with no persistent state.
OFFENSAI's Universal Offensive Ontology
One attack language. Every cloud.
UOO powers cross-cloud attack chain discovery that no single-platform logic can achieve.
One attack ontology across all clouds
Cross-cloud attack chains by design
From noise to chain signal
OFFENSAI cloud security validation you can trust

Human-initiated by design

Data sovereignty by design

Audit-ready output

Actionable remediation

Shift happens.
Be ready when it does.
Move from cloud exposure detection to controlled validation, technical evidence, and risk-based prioritization, powered by AI.