About OFFENSAI
Our mission is to push the boundaries of AI cloud security by building systems to understand, anticipate, and prove cloud attacks before they unfold.
How it began
OFFENSAI was founded in 2025 by offensive security engineers and cloud security leaders who noticed two current trends: general-purpose AI has gotten remarkably good at almost everything, but remains untrustworthy for the decisions security teams actually have to make; and cloud environments change every day at the speed of AI, while validation isn't keeping up.
A frontier model lacks the persistent context, domain reasoning, and proof that an AI security engine provides. It can summarize a risk, but it cannot be trusted to tell you, with evidence, whether an attacker can move from this identity to that data right now.
So, we built a system of specialized AI trained, not on the open internet, but on offensive tradecraft, identity and permission logic, and the specific structure of AWS, Azure, GCP, and Kubernetes. The system reasons like an experienced red teamer, chaining weaknesses into attack paths, and then proves them against your live environments. The result is a first-class continuous and autonomous cloud security testing solution, combining proprietary research and autonomous agents to discover, prove, and execute real attack paths.
Why security needs specialized AI
A general model can talk about your security. It can't be trusted to run it.

General AI is broad. Security is specific.
Frontier models optimize for broad reasoning and keep no persistent model of identities, trust relationships, or cloud attack chains. OFFENSAI is trained on security.

General AI infers. Security demands proof.
Ask a general model if you're exposed and get a plausible guess. OFFENSAI walks attack paths in your live environment and shows what worked, what failed, and where controls intervened.

General AI forgets. Security is continuous.
A prompt resets context every time. OFFENSAI maintains persistent intelligence across every cloud change and every validation, so coverage compounds instead of restarting.
What makes OFFENSAI different?
Purpose-built AI, continuous validation, and a moat other security tools can't claim.
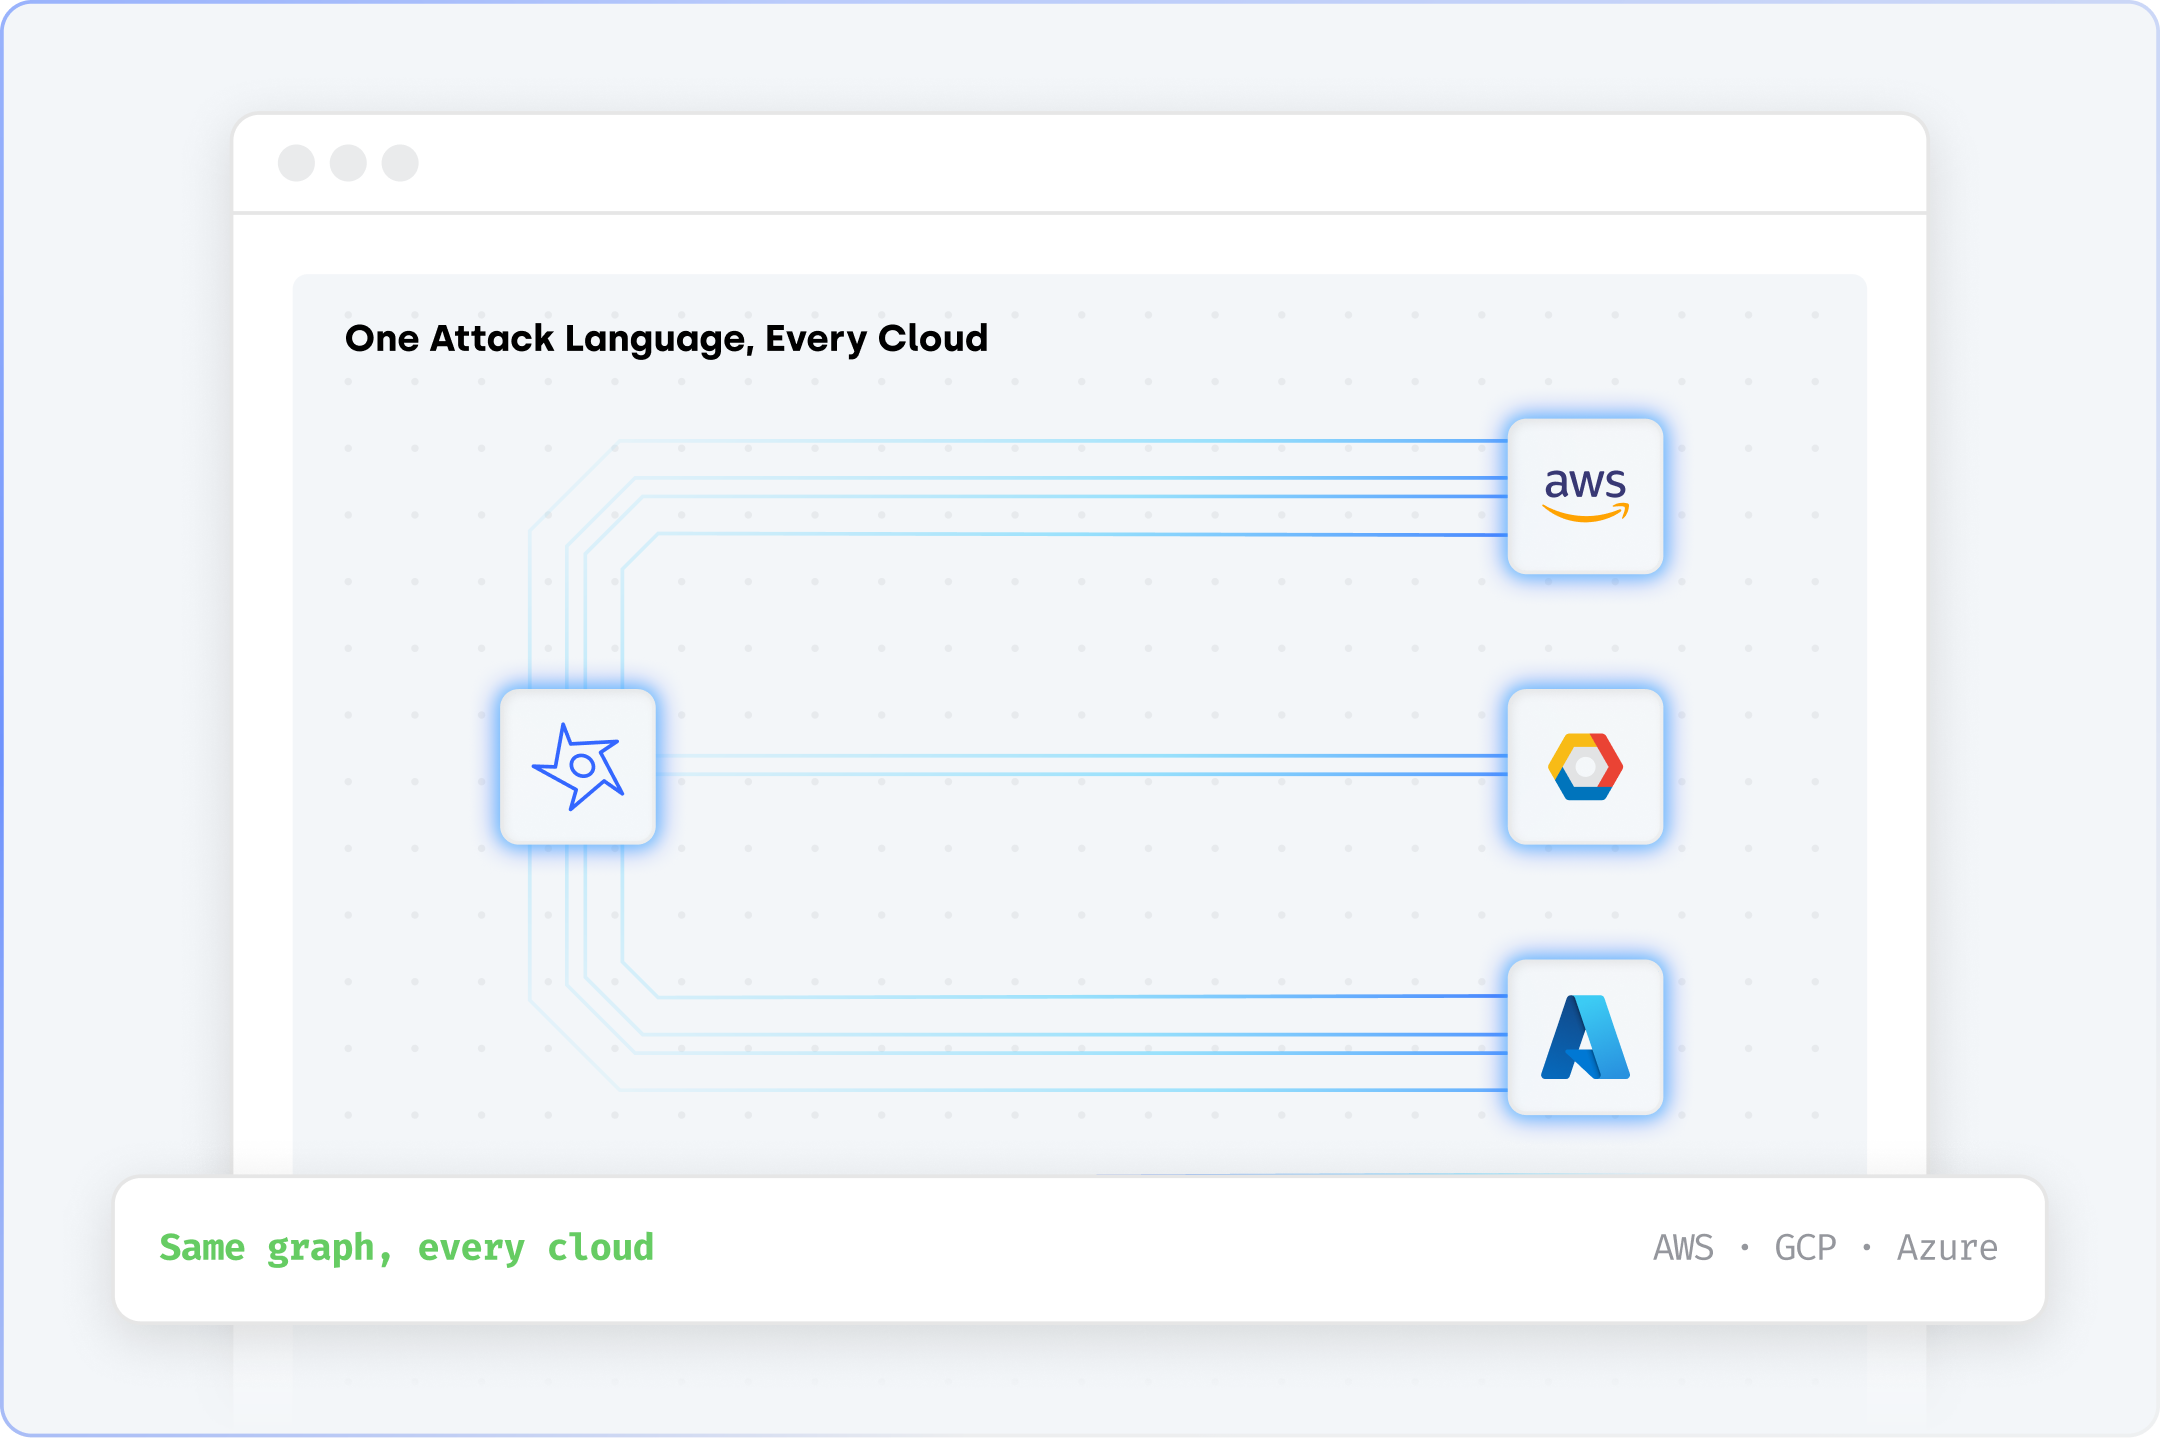
One attack language across every cloud
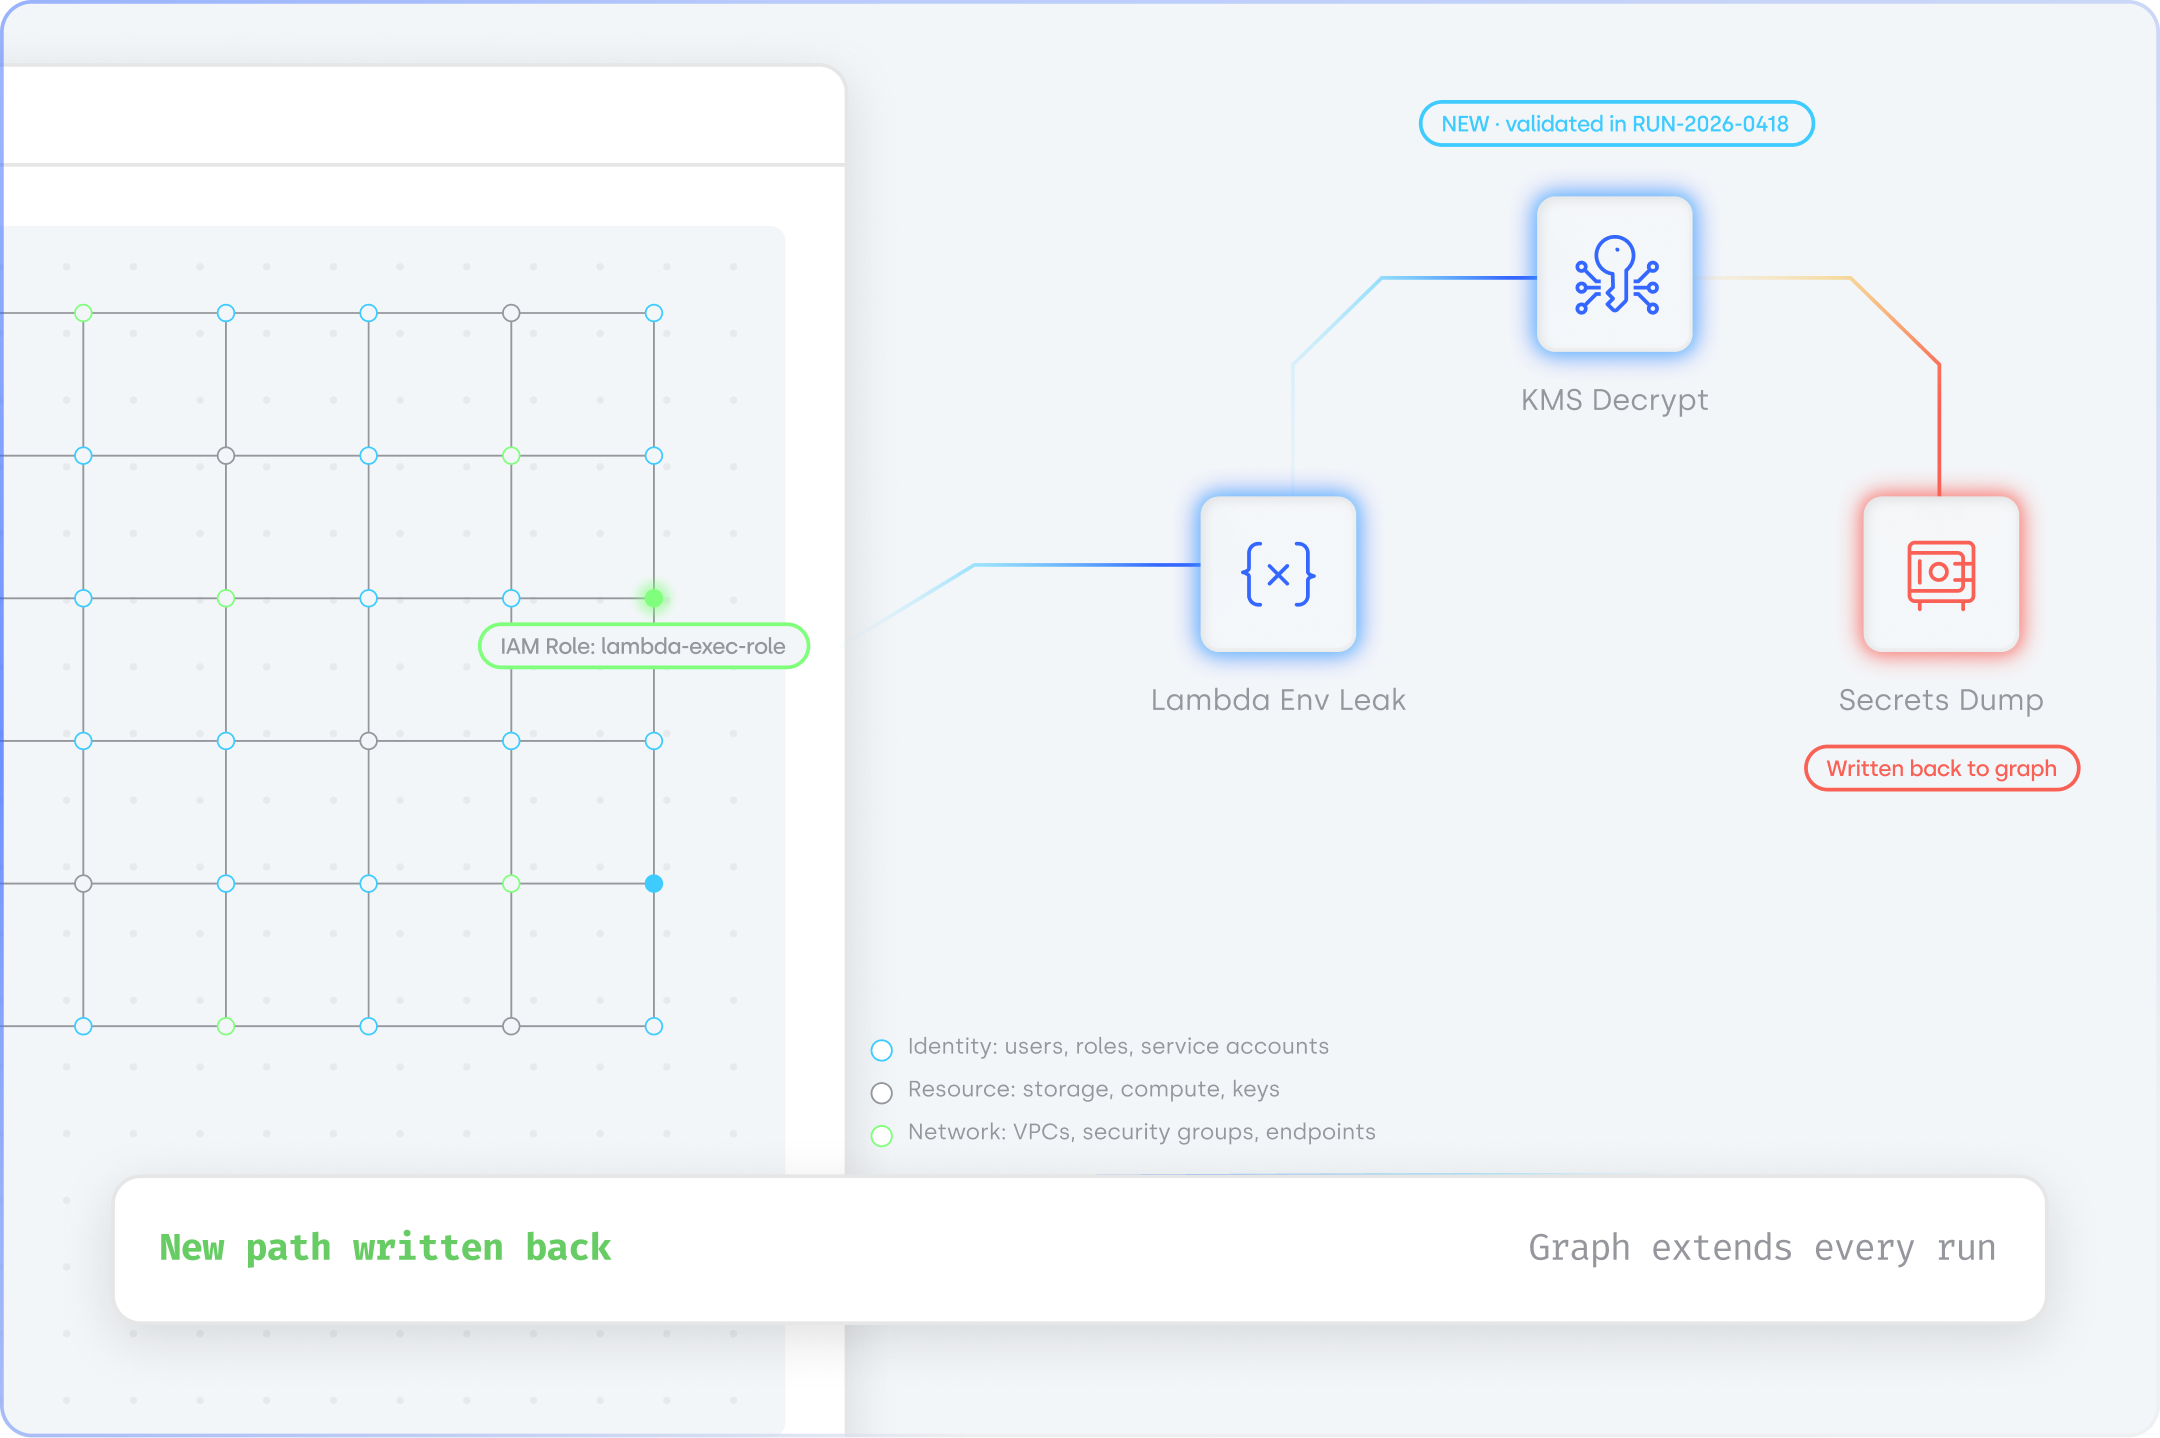
OFFENSAI's Universal Offensive Ontology reduces AWS, Azure, GCP, and Kubernetes to shared attack primitives, enabling cross-cloud attack paths that single-provider tools can't see.
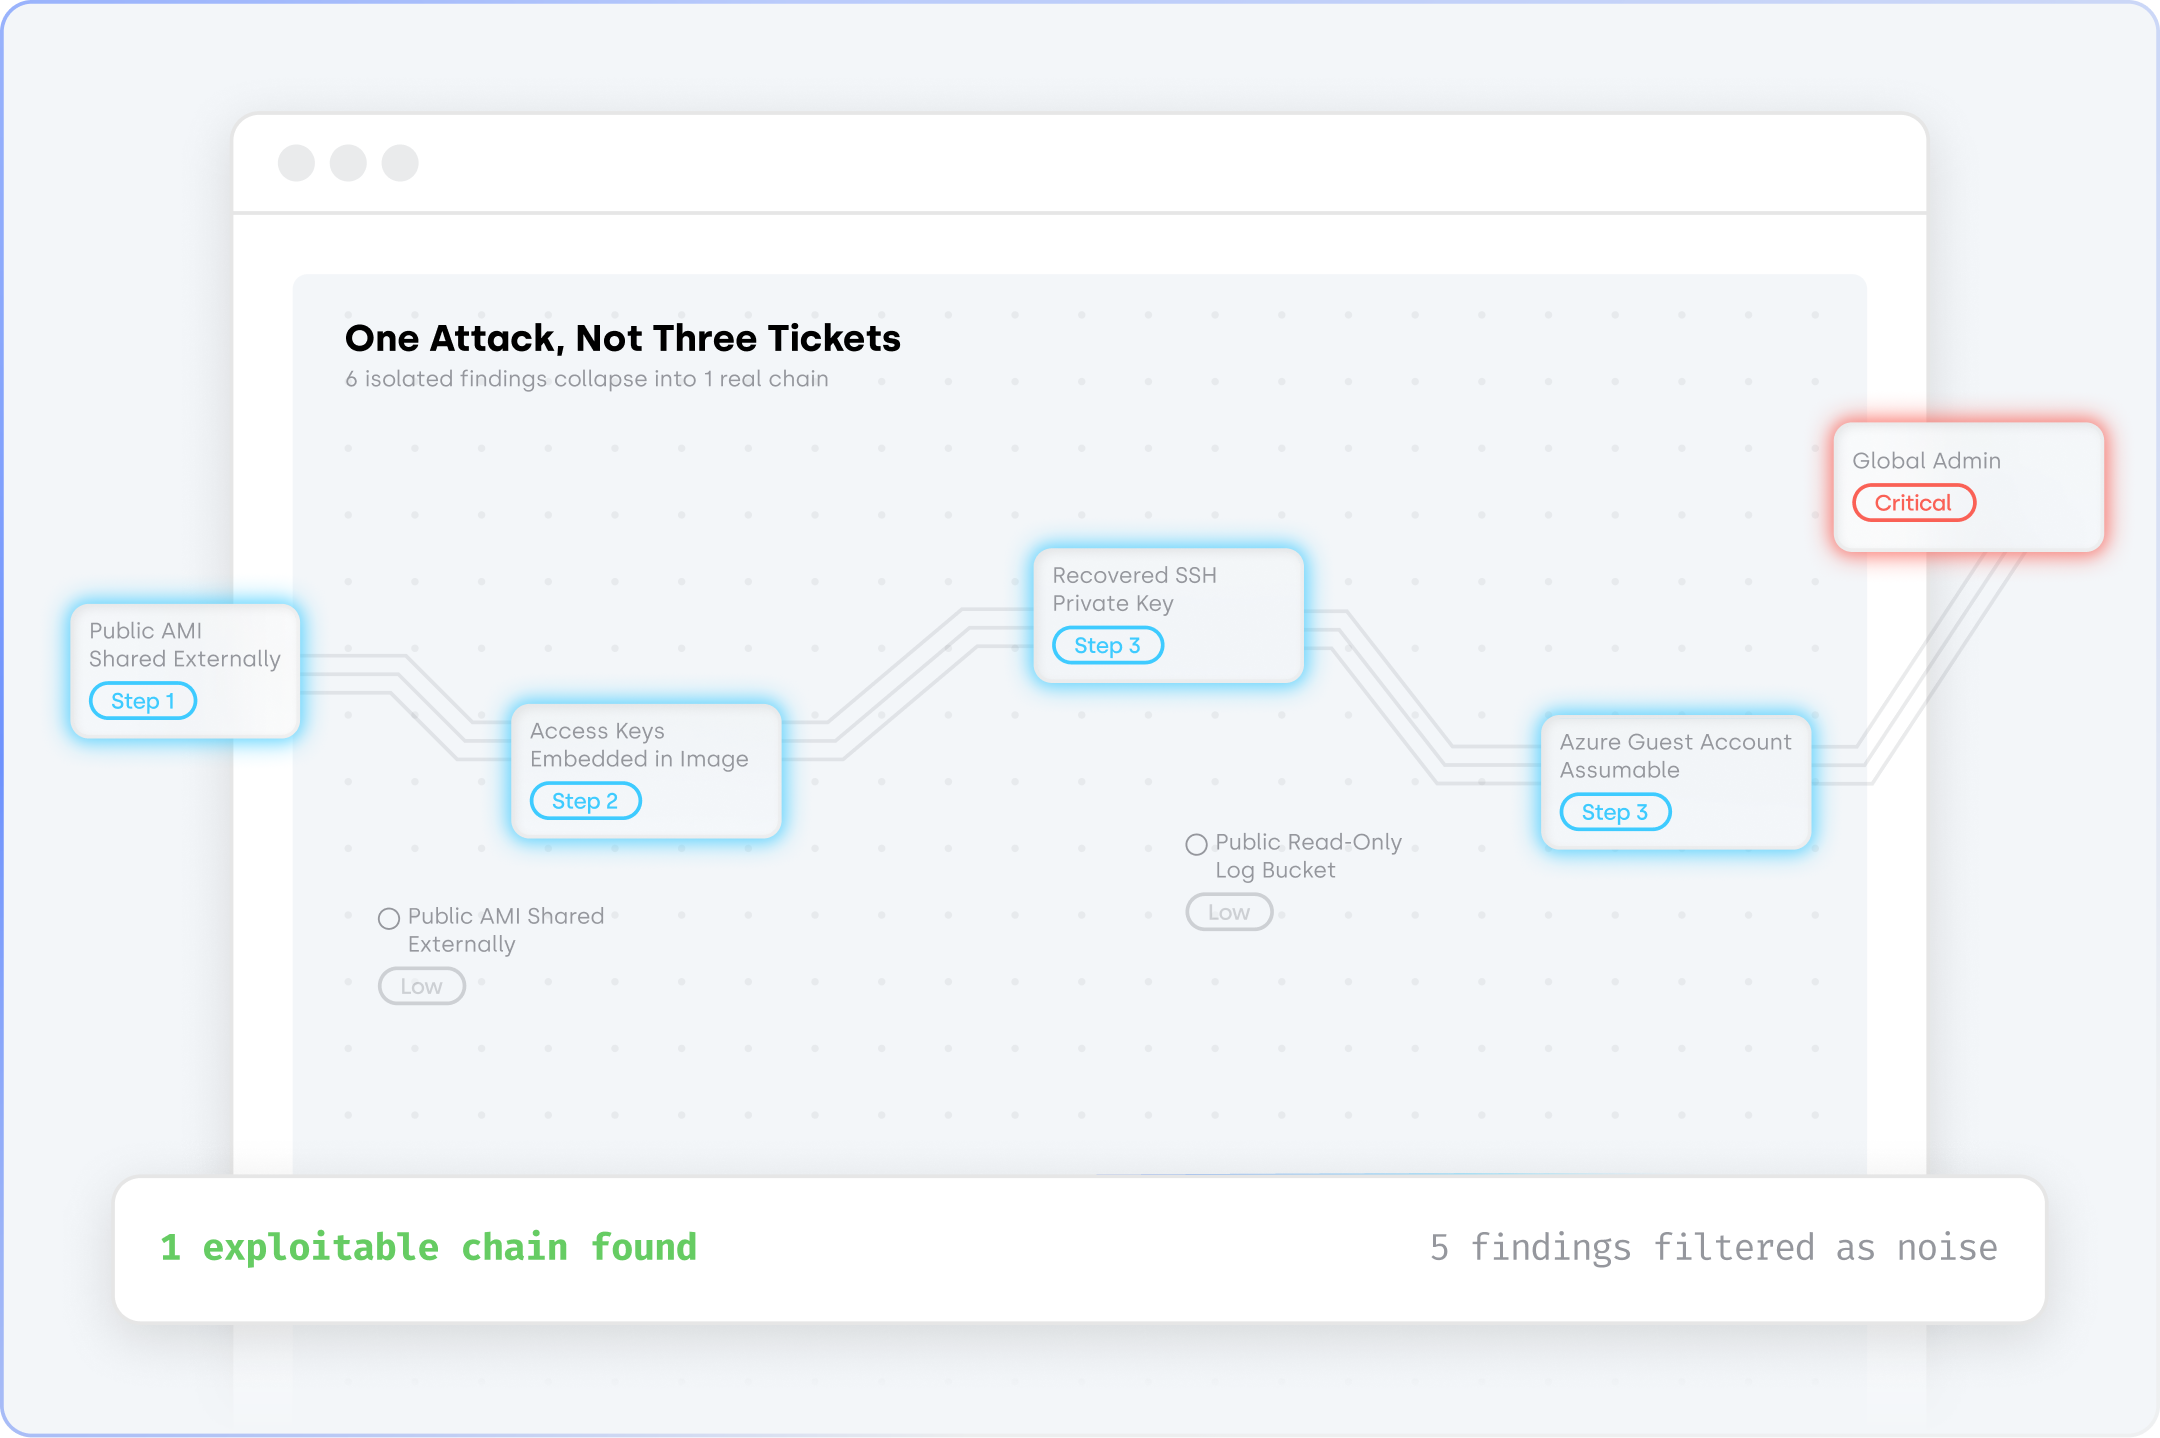
Real attack chains, not isolated findings
Cloud breaches happen through sequences. OFFENSAI surfaces the toxic combinations a single-resource scanner scores as three separate "low" findings and misses entirely.
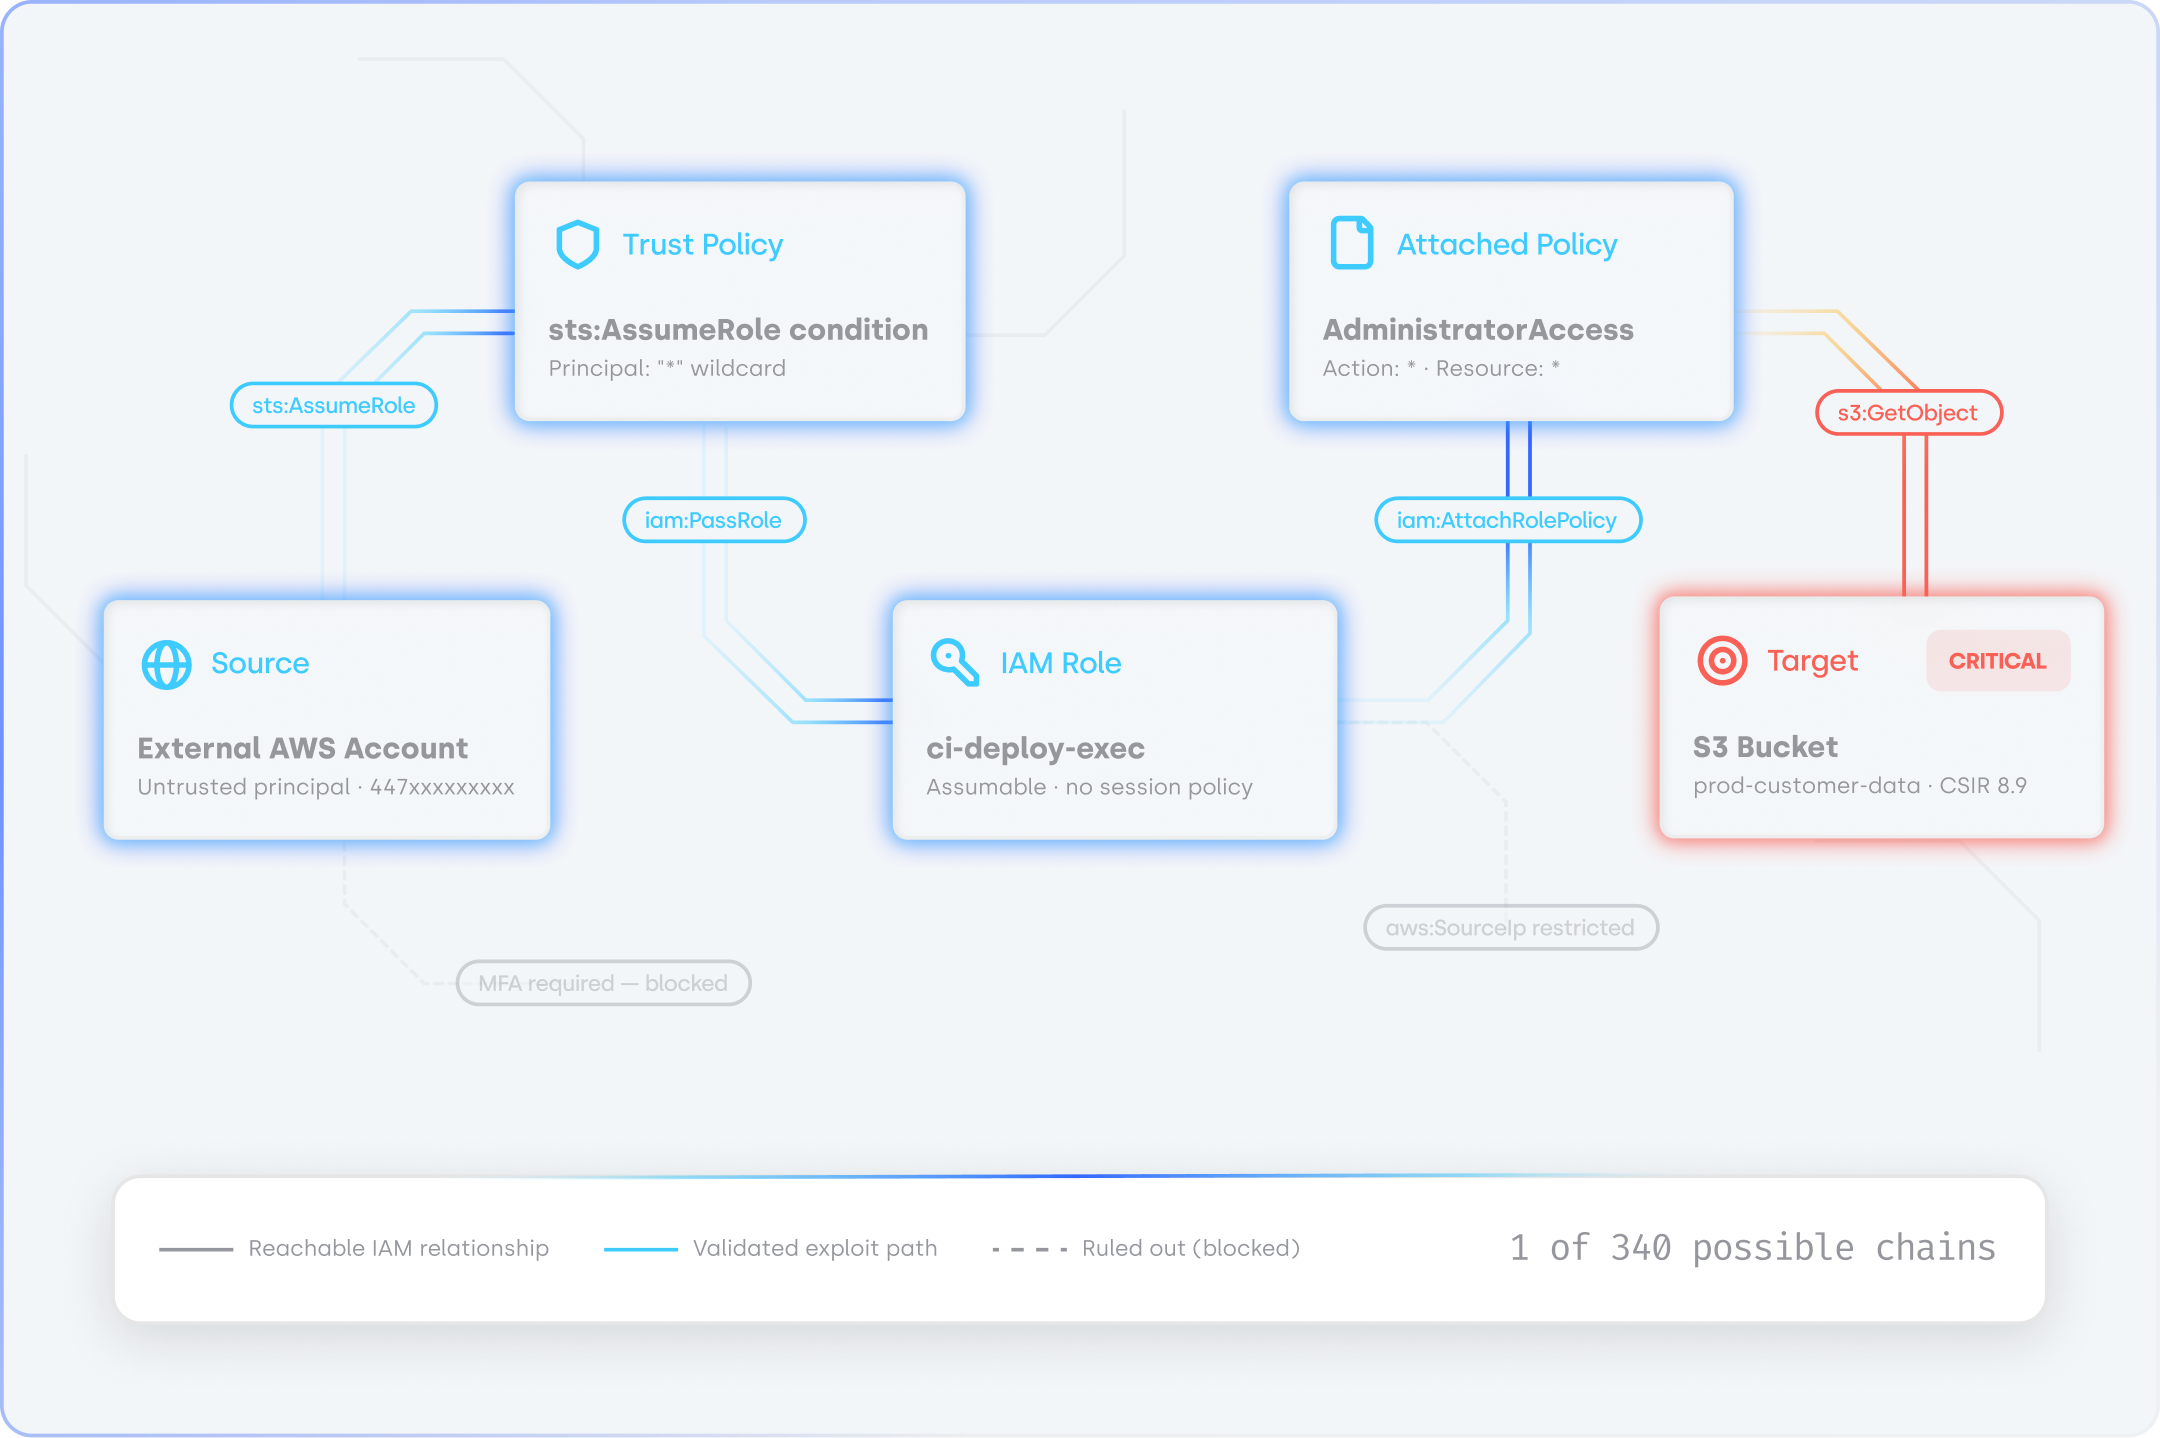
Every finding comes with receipts
We provide the exact IAM permissions, trust relationships, and validation proof — the evidence that holds up in technical reviews, executive discussions, audits, and incident response.
It gets smarter on its own
OFFENSAI learns from cloud changes, new techniques, and validations, increasing coverage without manual updates so today's protection is smarter than yesterday's.

Attacker-grade AI, run responsibly

Safe by design
Validations run only on human approval. We connect through native cloud APIs with no host agents to deploy and read-only access by default.

Research is part of the product
Our original offensive research, including the attack ontology that powers the models, feeds directly back into how customers test.

We help teams move fast
A finding matters only if it drives action. Each validated path includes clear evidence and remediation guidance, mapped to MITRE ATT&CK, NIST, and SOC 2.
The people behind the model
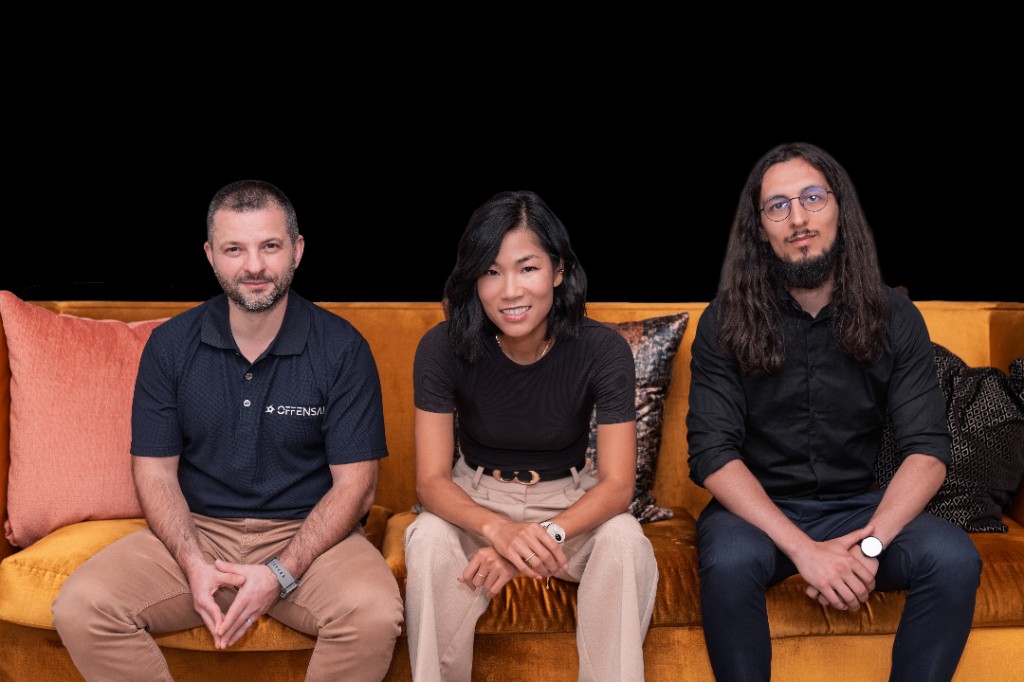
OFFENSAI is led by offensive security researchers and cloud engineers who have spent their careers studying how cloud attacks work. Our thesis is that a specialized model beats a general one, so it matters who trains it.


Shift happens.
Be ready when it does.
Move from cloud exposure detection to controlled validation, technical evidence, and risk-based prioritization, powered by AI.