Cloud red teaming that never sleeps
Continuously uncover and validate multi-step attack chains across cloud environments with OFFENSAI's autonomous AI agents. Track how real attackers move inside clouds, then prove which paths actually work.

Why cloud exploitation demands specialized validation

Technique-level coverage

Evidence that supports compliance

Threat-informed by default
Attacker-grade capabilities, built for the cloud
Get continuous red teaming with autonomous engines that discover, execute, and validate real attack chains. Expose exploit paths, test defenses, and get evidence you can act on.
Adaptive AI red teaming engine
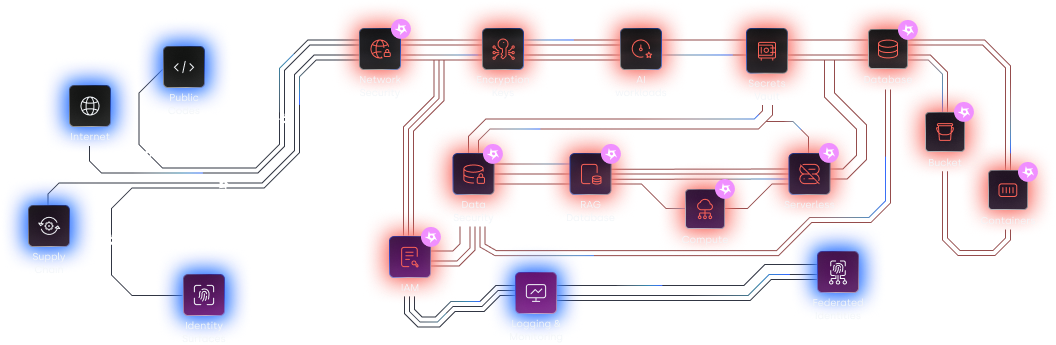
Execute real adversarial behavior in your cloud, not scripted tests. The Adversary Attack Engine performs IAM abuse, privilege escalation, and lateral movement to generate verified kill chains.
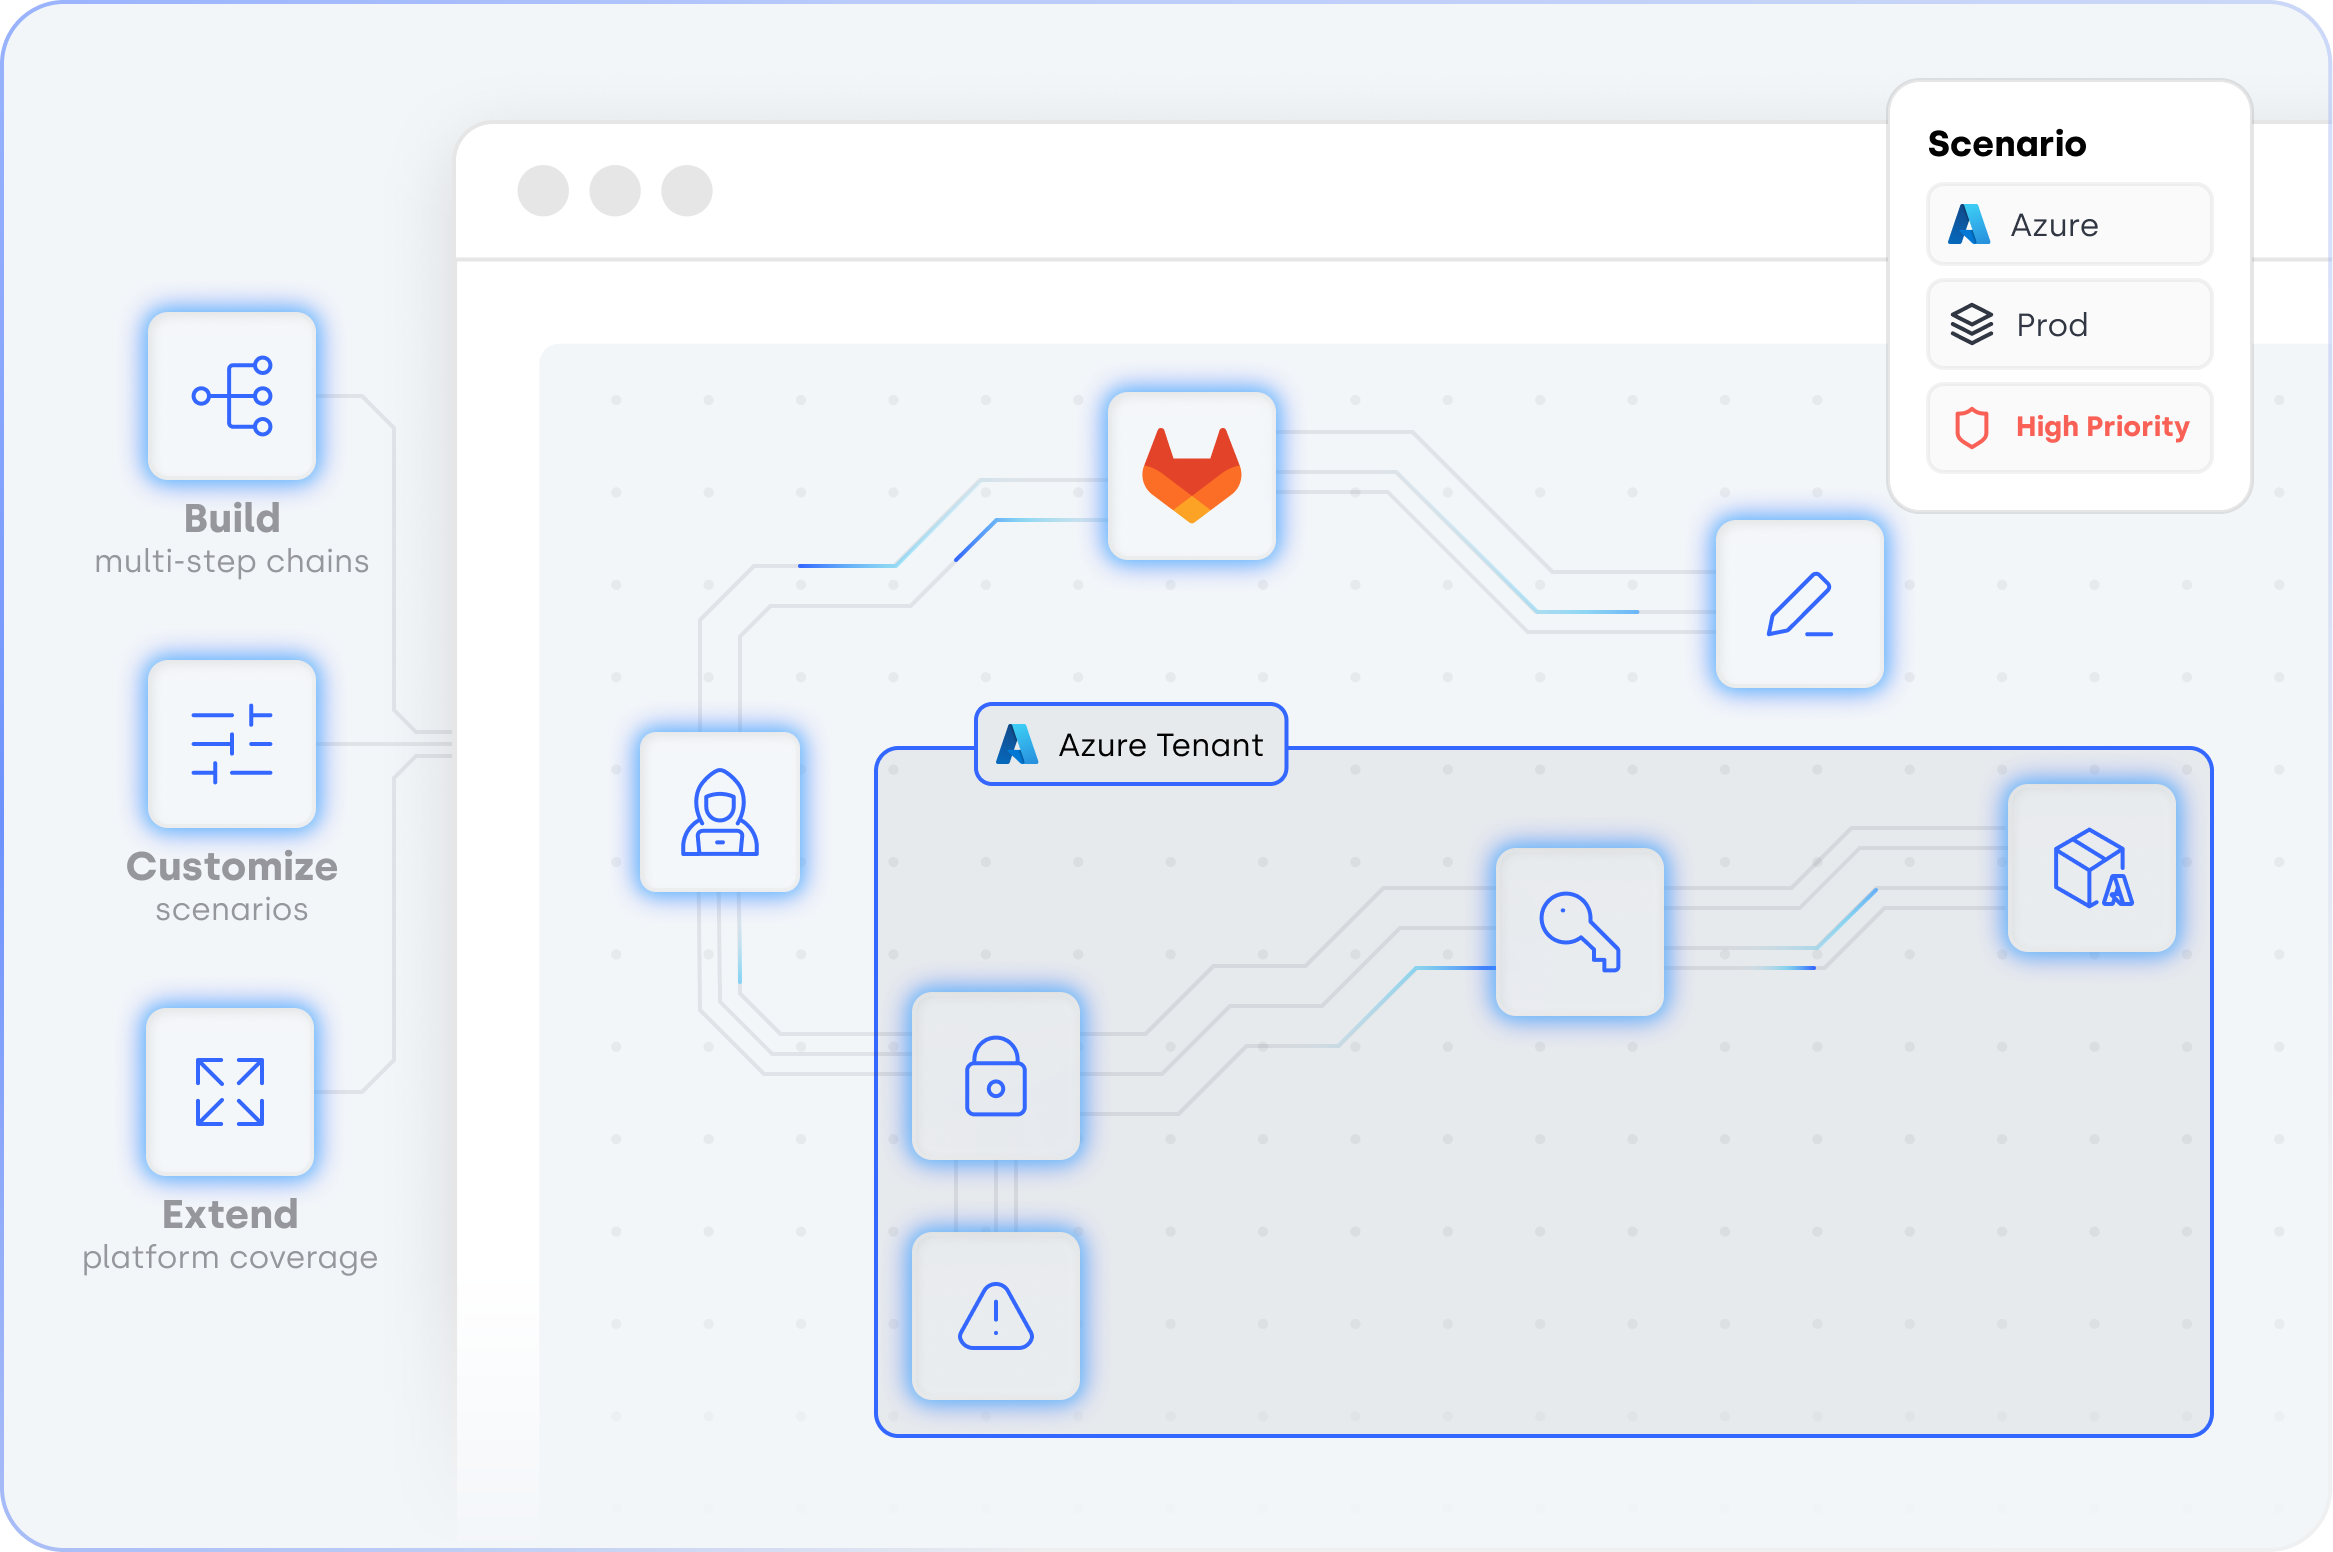
Morphed attack path generation
Expose the many ways attackers reach the same target. OFFENSAI mutates attack paths per your environment, revealing alternate privilege chains and lateral movement routes missed by static red team scenarios.
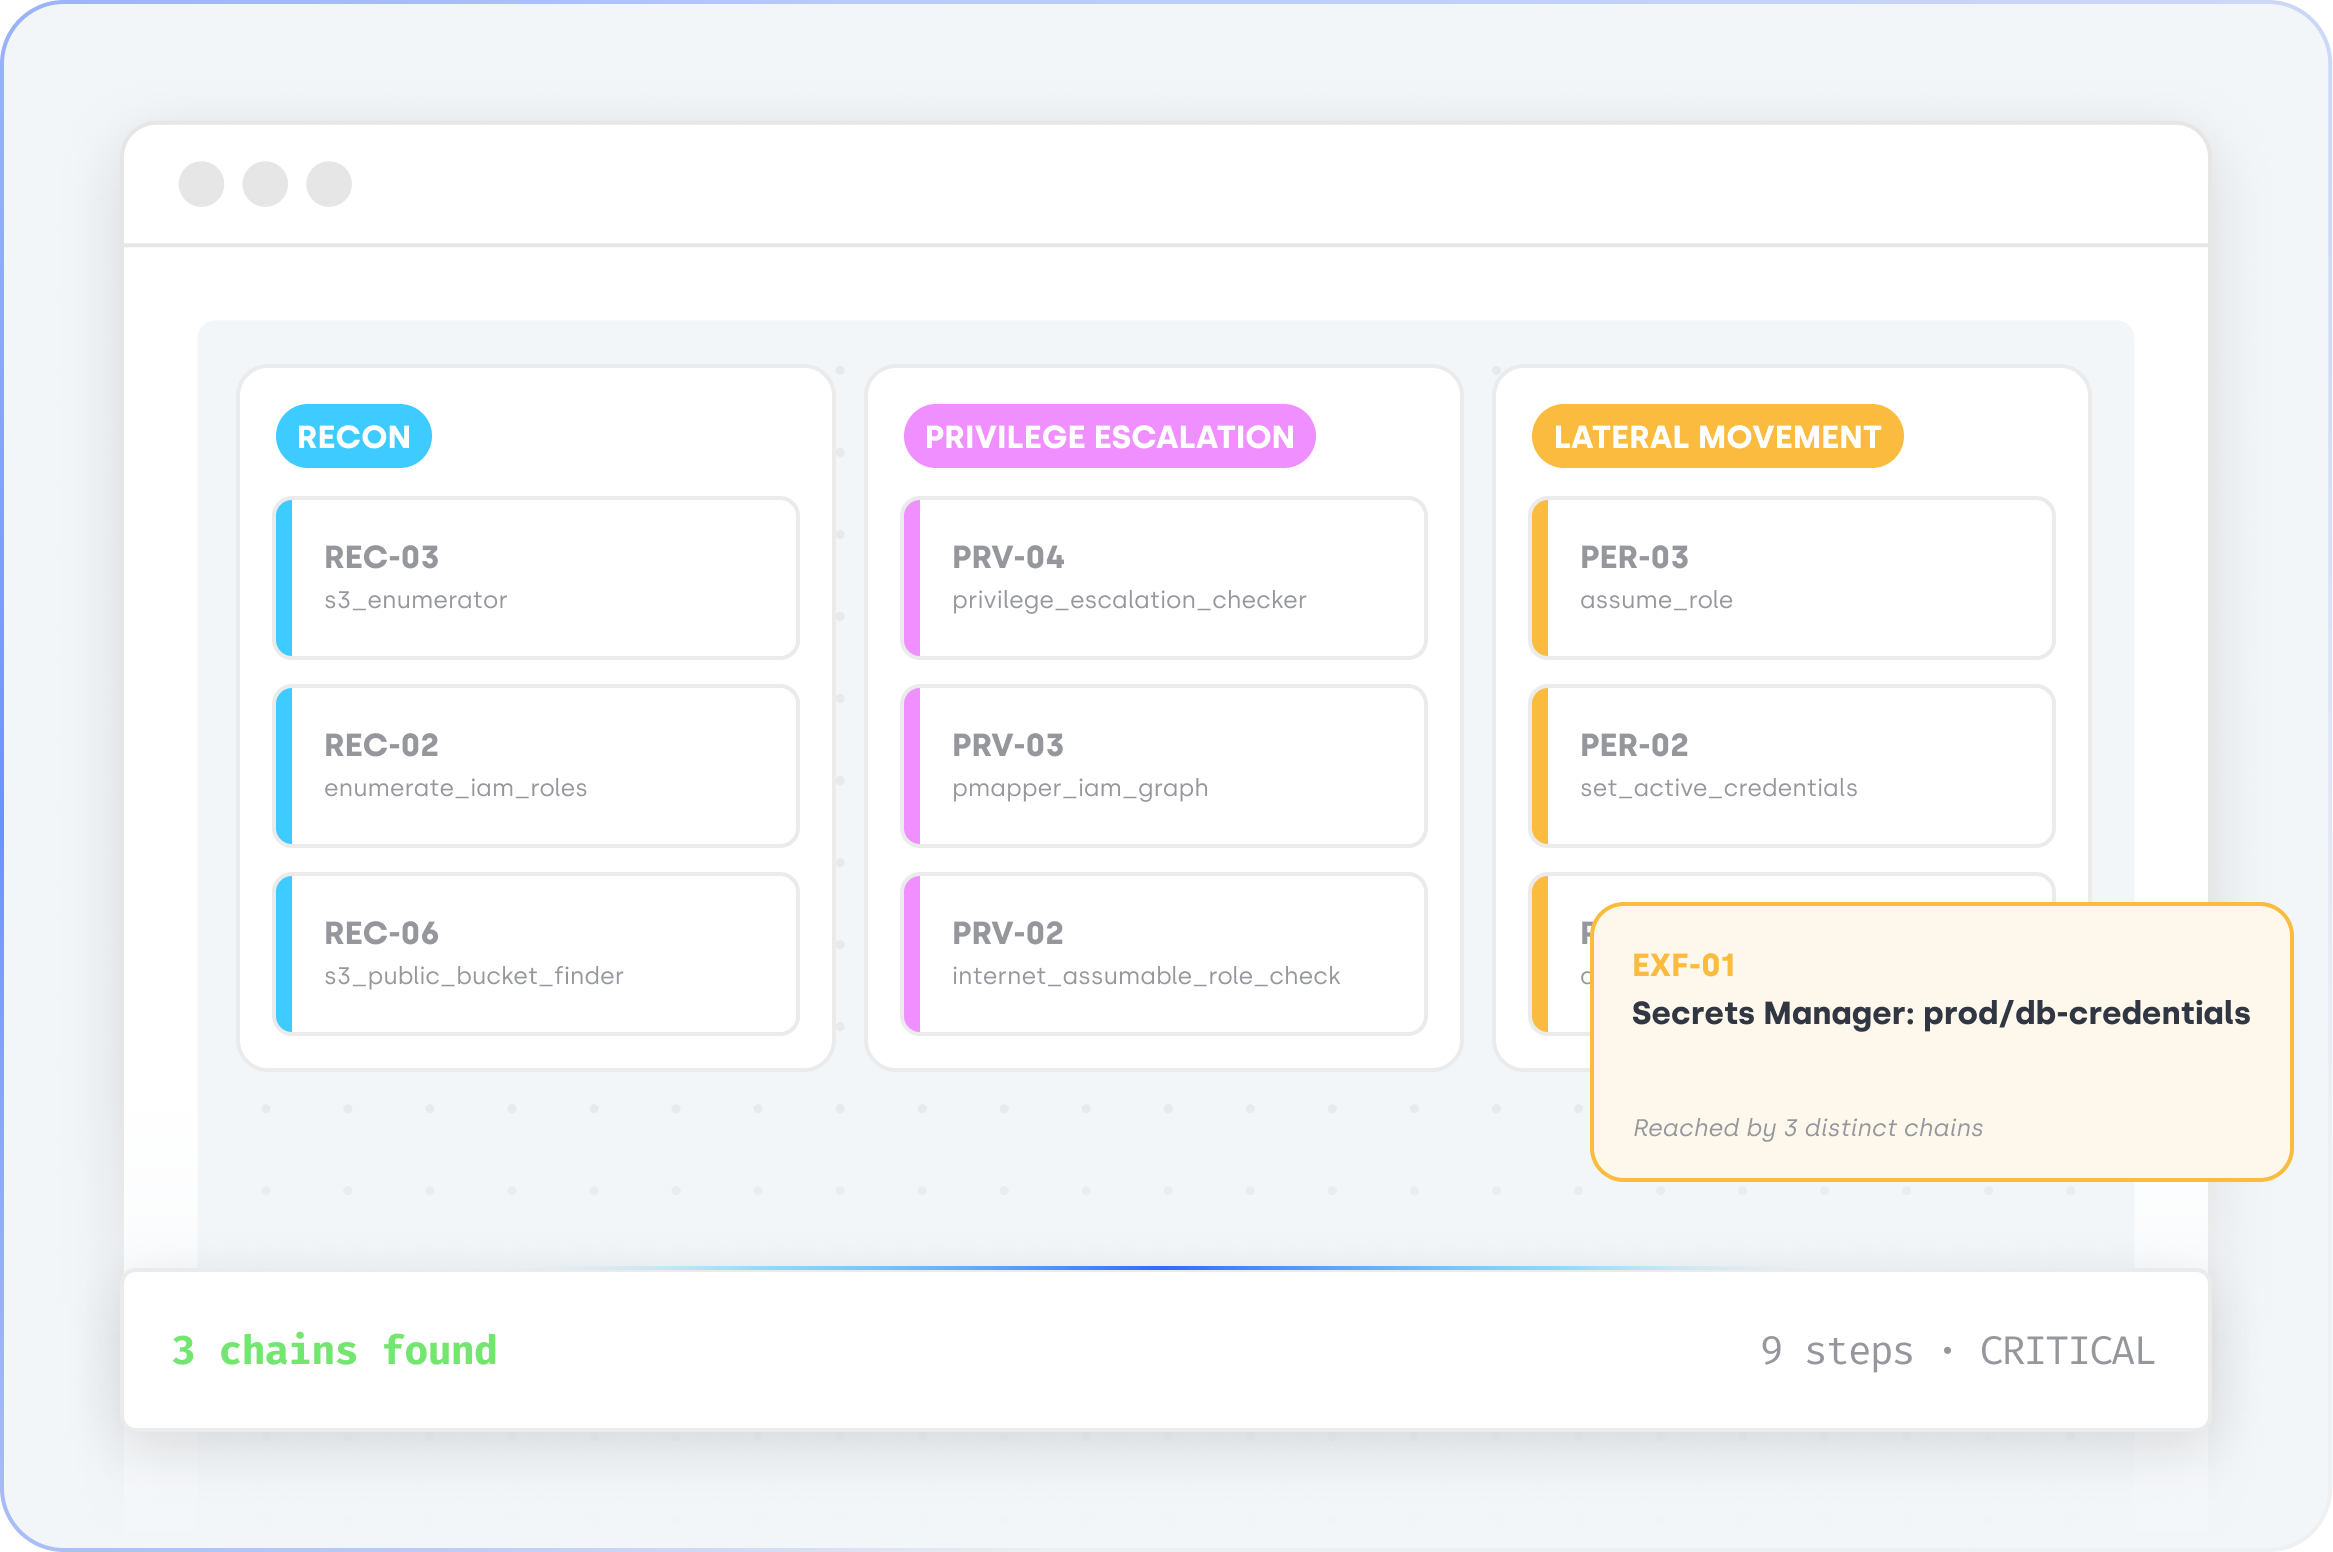
Continuous adversarial validation loop
Maintain 24/7 assurance for your defenses. Agent O, OFFENSAI's autonomous agent, and the Evasion Engine continuously re-execute attack paths, test detection coverage, and produce compliance-ready proof.
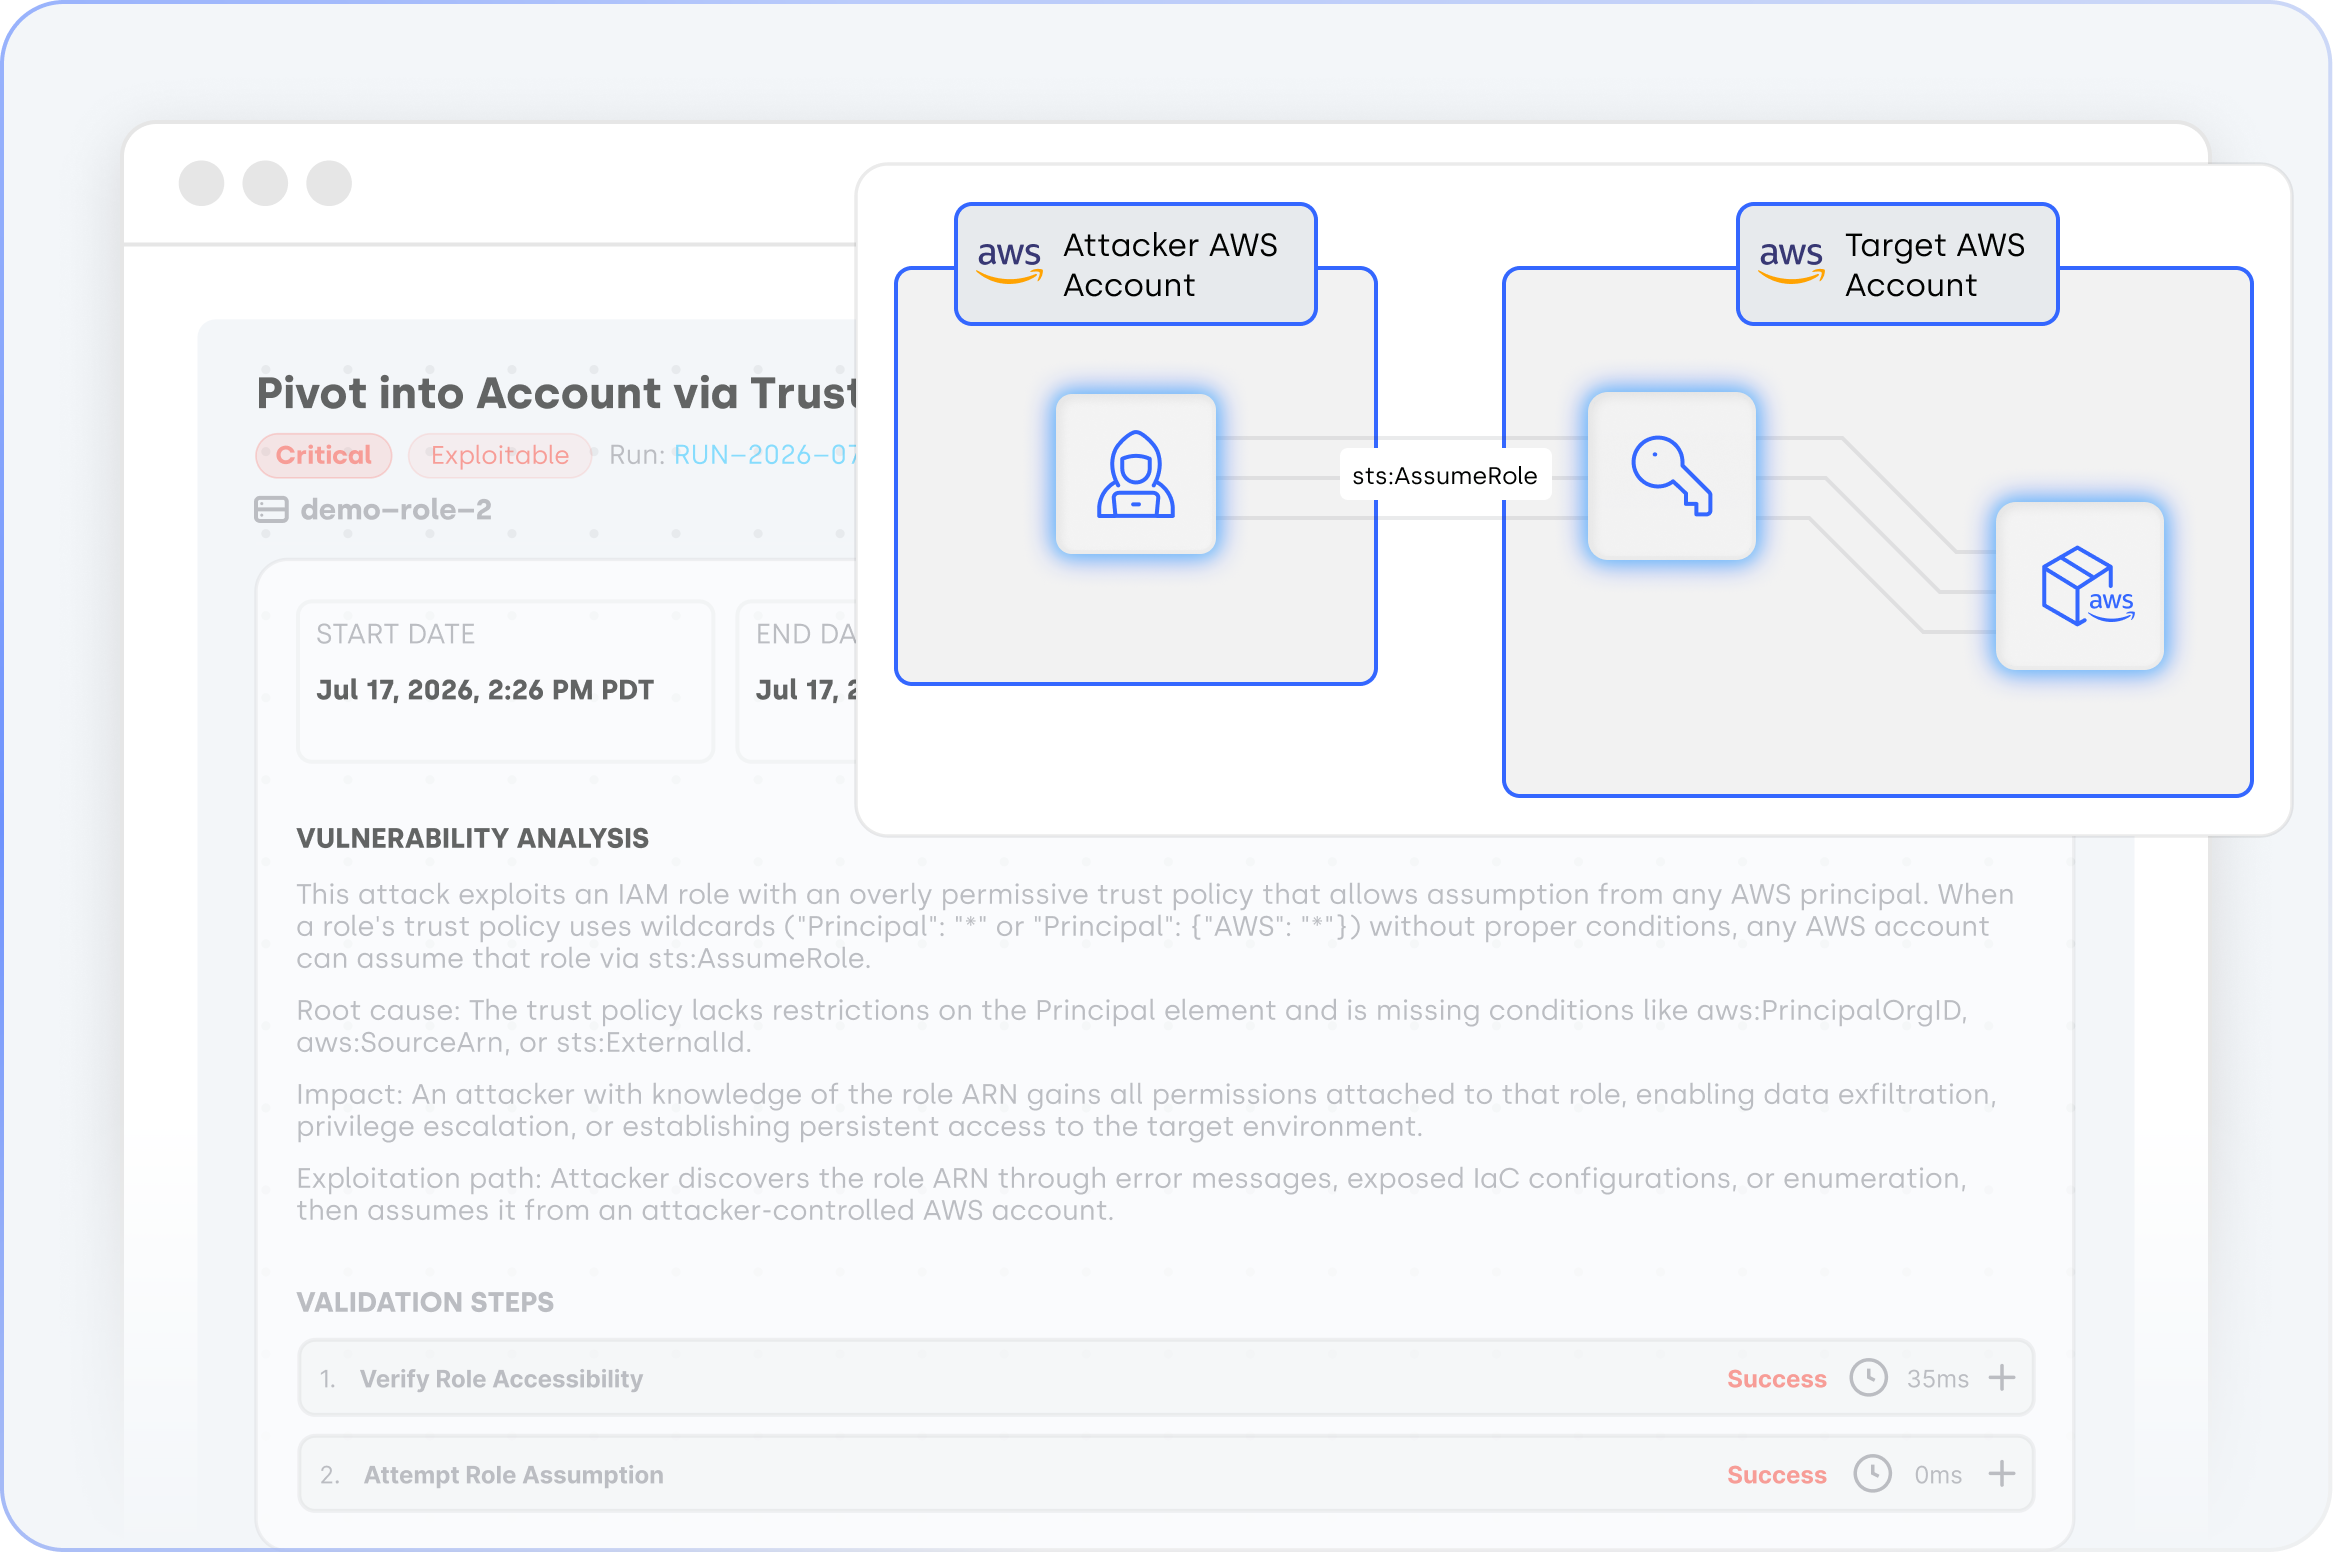
Proven impact at machine speed
From connection to first validated attack path, with no setup delays or agent deployment required.
Reduce dependence on manual pentests and traditional red team engagements by validating continuously in-platform.
Maintain continuous assurance as cloud identities, permissions, and configurations change over time.
Accelerate detection and remediation by turning attack paths into validated findings with clear next actions.
OFFENSAI cloud security validation you can trust

Human-initiated by design

Data sovereignty by design

Audit-ready output

Actionable remediation

Shift happens.
Be ready when it does.
Move from cloud exposure detection to controlled validation, technical evidence, and risk-based prioritization, powered by AI.